AI leaders keep telling us the future of work is about to change forever… yet they rarely offer more than vague predictions. Continue reading “This Tool Forecasts New Jobs That AI Will Create”
AI leaders keep telling us the future of work is about to change forever… yet they rarely offer more than vague predictions. Continue reading “This Tool Forecasts New Jobs That AI Will Create”
I’m working on a C# project, using a SQL Server database. I have been asked to add the possibility to work with another database.
The current database handling is done via some <db_Name>DB.dbml files and their corresponding files, so I’d like to have some file like that for the new database.
First, I have created the *.dbml file myself, I’ve added a corresponding *.layout file but that seems not to work out.
Then, I figured “Why not let Visual Studio such a file and I will fill it in afterwards”, but this led me to this other question, where the accepted answer mentions doing an “Add new item”, and then make the right choice in the “Data” chapter (“Linq-to-SQL classes”), but I believe this screenshot clearly explains my problem:

Now I have two choices:
*.dbml files (and layout and designer files) manually and hope I will get it to work.LinQ-to-SQL feature (or its replacement).Can anyone give me a clue? And in case LinQ-to-SQL is replaced by another feature, what’s the name?
Smartwatch shipments in India dipped annually for the first time in 2024, as consumers moved away from cheap, unknown brands. Apple bucked the broader trend, however, with a reported 2.4x growth for the year.
According to data from analyst firm Counterpoint, India’s smartwatch shipments dropped 30% year-on-year in 2024. Signs of slowing sales emerged last year, as the market was flooded with unknown brands. The trend aversely impacted established domestic players, slowing the pace of innovation as a result.
As the broader market faltered, Apple Watch saw a 141% increase in its shipments last year. That growth bucked a 57% decline for the company in 2023, according to Counterpoint.

Counterpoint senior analyst Anshika Jain told TechCrunch that the Apple Watch saw an uptick last year as, “some experienced users gradually moved to advanced smartwatches” for better health insights, smartphone integration, and other features absent on cheaper devices.
“We expect this growing trend to continue in 2025,” she added.
The growth in Apple Watch shipments aligns with the the iPhone’s expanding marketshare in the country. Apple emerged as one of the top-five smartphone vendors in India last year, with a roughly 10% share in in Q4.
However, Apple Watch’s sizable growth ultimately had little impact on its overall share of the 35 million smartwatches shipped in India last year, according to IDC. Counterpoint, which does not share absolute shipment figures, told TechCrunch that the Apple Watch comprised roughly 2% of India’s entire smartwatch market in 2024.
Apple Watch’s success boosted overall premium smartwatch (priced above $230) shipments in India, with 147% growth. The Series 10 was the top model, followed by the Series 9. The Apple Watch cumulatively captured 50% of the total premium smartwatch segment in the country, per Counterpoint.
Samsung and OnePlus were the other top players in the premium segment last year, with a 4% and 1% market share, respectively.

Andy Walker / Android Authority
I’m always in two minds about tapping a link on my Android phone. It could lead me to an innocuous duck meme that makes my day. Alternatively, it could also usher me somewhere I don’t quite want to go. This is less likely on platforms where I can actively preview the link in full, but for many other apps, there’s no telling where that blue hyperlinked text will lead you.
I use the open source URLCheck, one of my favorite Android apps, to address this potential security lapse. After discovering it several months ago, it quickly became one of the first and most important apps I install on new and old Android devices.
9 votes

Andy Walker / Android Authority
URLCheck is a tiny Android app that gives me more control over links than Android. On the surface, it’s a middleman that intercepts links and allows me to view them in full, but if you dig a little deeper, it lets users modify them and even check them for viruses using the URL Scanner module with a VirusTotal API key (you’ll have to sign up to provide your own). Android natively offers none of these features, so URLCheck is a critical security addition to any smartphone.
URLCheck intercepts links before they’re followed, allowing me to view them, modify them, or disregard them entirely.
It also has other utility, too. Set it as your default web browser, and URLCheck lets you pick a browser or app to open the link. For instance, if I open a link from Gmail, URLCheck will intercept it and allow me to open it in Chrome, Firefox, my local shopping app, or any other related app I’ve installed. Without URLCheck, the link would open in whatever default browser I have set. As I use multiple browsers on my phone, including Chrome for personal Google-related data and Firefox for day-to-day browsing, I hugely appreciate getting the option to choose.
URLCheck also offers its powers when sharing links. I find it fantastic for removing tracking tags and unnecessary redirects before passing them on to friends and family. There’s nothing worse than receiving a random link obfuscated by layers of redirects.
URLCheck can be a little overwhelming to set up, but its customizability makes it malleable. The app offers a straightforward tutorial that walks you through the core steps to enhance your experience. It’s foolproof, but I suggest you follow the quick rundown below.
Now, whenever you select a URL in an Android app, URLCheck shows you exactly where it points. You can then follow that link, modify it, or choose another route entirely.
Don’t get me wrong. URLCheck is powerful, but it won’t nanny you around the web. The app doesn’t act as an alarm. It won’t warn you if a link is dodgy unless you use its URL Scanner module. Without this module active, you’ll have to use some of your natural smarts to determine if the destination is somewhere you want to go.
URLCheck won’t warn you if a link is bad unless you use its URL Scanner module.
Additionally, to check a URL within your browser, you must use the share menu to share the link to URLCheck. During regular operation, the app only intercepts links from apps that would direct to your browser.
Notably, if you find that URLCheck doesn’t open links and instead that link opens directly in another app, you’ll need to change the way that particular app handles web links. For instance, my shopping app hijacks these links on my Pixel. To fix this, I navigated to Settings > Apps > See all apps > find and tap on the offending app > Open by default > check In your browser. Now, as the default browser, URLCheck intercepts these links.
Do you use URLCheck or another link-checking tool? Let me know in the comments below.
To better prepare communities for extreme weather, forecasters first need to see exactly where it’ll land.
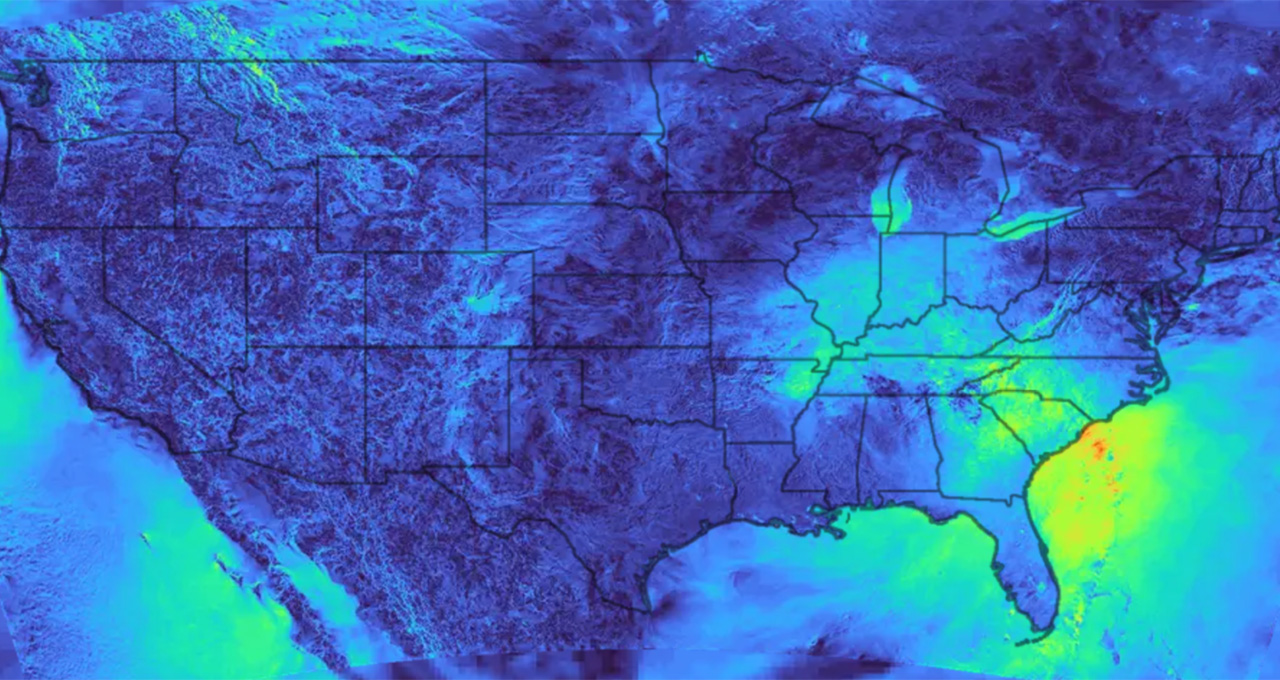
That’s why weather agencies and climate scientists around the world are harnessing NVIDIA CorrDiff, a generative AI weather model that enables kilometer-scale forecasts of wind, temperature, and precipitation type and amount. It’s part of the NVIDIA Earth-2 platform for simulating weather and climate conditions.
The paper behind CorrDiff was featured today in Communications Earth and Environment, part of the Nature portfolio of scientific journals. Available as an easy-to-deploy NVIDIA NIM microservice, the model is already being used by weather technology companies, researchers and government agencies to enhance their forecasts.
With the rising frequency of extreme weather events, fast, high-resolution predictions of weather phenomena could help mitigate risks to people, communities and economies by supporting risk assessment, evacuation planning, disaster management and the development of climate-resilient infrastructure.
Weather agencies and startups across the globe are adopting CorrDiff and other Earth-2 tools to improve the resolution and precision of forecasts for extreme weather phenomena, renewable energy management and agricultural planning.
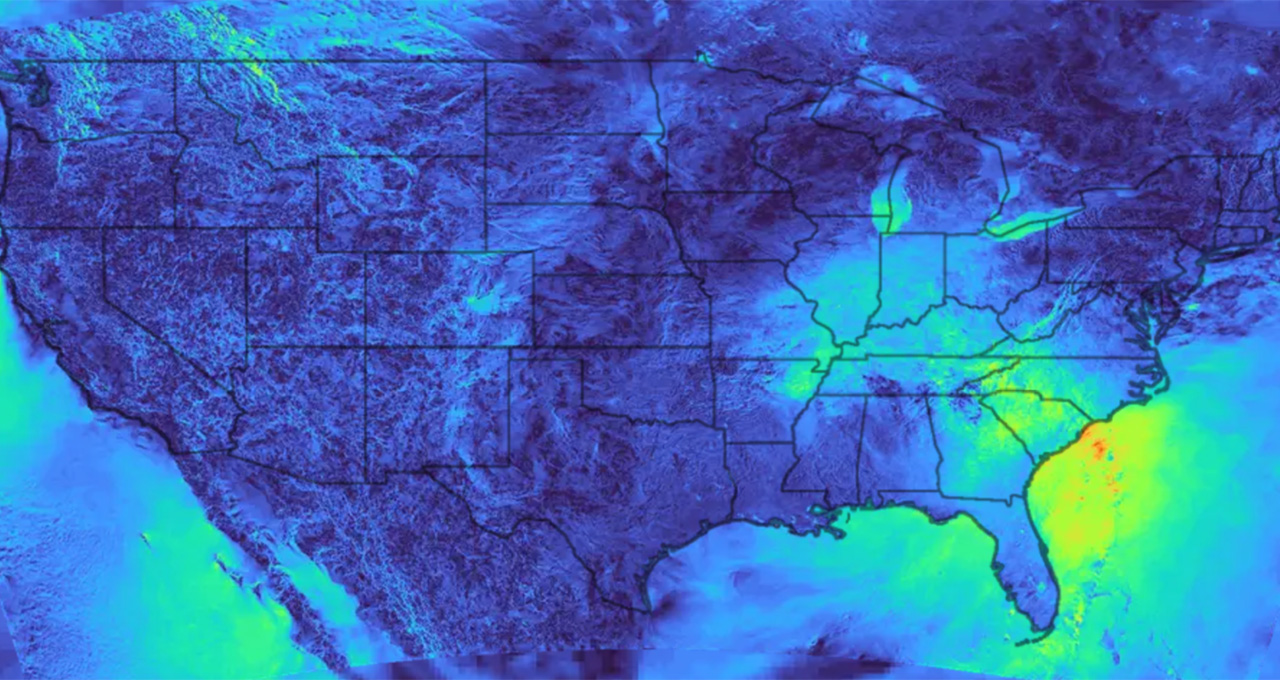
CorrDiff uses generative AI to sharpen the precision of coarse-resolution weather models — resolving atmospheric data from 25-kilometer scale down to 2 kilometers using diffusion modeling, the same kind of AI model architecture that powers today’s text-to-image generation services.
In addition to boosting image resolution, CorrDiff can also predict related variables that weren’t present in the input data — such as radar reflectivity, which is used as an indicator of rain location and intensity.
CorrDiff was trained on the Weather Research and Forecasting model’s numerical simulations to generate weather patterns at 12x higher resolution.
The initial CorrDiff model, announced at NVIDIA GTC 2024 and described in the Communications Earth and Environment paper, was optimized on Taiwan weather data in collaboration with its Central Weather Administration.
NVIDIA researchers and engineers next worked to efficiently scale the model to cover a larger section of the globe. The version released as an NVIDIA NIM microservice at Supercomputing 2024 covers the continental United States — trained on U.S. weather data, with sample datasets of real-world natural disasters including hurricanes, floods, winter storms, tornados and cold waves.
The optimized CorrDiff NIM microservice for U.S. data is 500x faster and 10,000x more energy-efficient than traditional high-resolution numerical weather prediction using CPUs.
The research team behind CorrDiff continues to advance the model’s capabilities, and has released additional generative AI diffusion models showing how the model could be enhanced to more robustly resolve small-scale details in different environments — and better capture rare or extreme weather events.
CorrDiff could also help with downwash prediction — when strong winds funnel down to street level, damaging buildings and affecting pedestrians — in urban areas.
Meteorological agencies and companies around the globe are tapping CorrDiff to accelerate predictions with applications in regional forecasting, renewable energy and disaster management.
Taiwan’s National Science and Technology Center for Disaster Reduction, for instance, has deployed the CorrDiff to support disaster alerts in the region, enabling an estimated gigawatt-hour of energy savings due to the energy efficiency of CorrDiff running on the NVIDIA AI platform. CorrDiff predictions are embedded in the center’s disaster monitoring site, helping Taiwan forecasters better prepare for typhoons.
Learn more about AI applications using Earth-2 at NVIDIA GTC, the global AI conference taking place March 17-21 in San Jose, California. Relevant sessions include:
Learn how AI is transforming climate science in the TEDx talk below by Mike Pritchard, director of climate simulation research at NVIDIA:
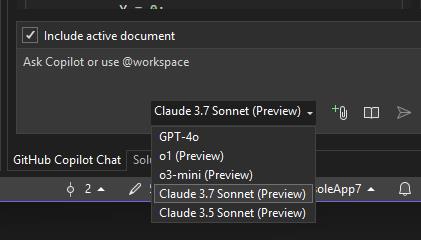
The world of AI is evolving at a breathtaking pace, and today brings an exciting milestone for developers and tech enthusiasts alike. Anthropic’s newest release, Claude 3.7, is now available directly within GitHub Copilot for Visual Studio 2022 17.13, heralding a new era of seamlessly integrated, advanced AI coding assistance. This new Sonnet model supports the non-thinking modes in Copilot.

Getting started is easy:
If you don’t see Claude 3.7 as an option, there could be two reasons:
For further details, check out the Using Claude Sonnet in Copilot Chat – GitHub Docs.
We’re super excited about this enhancement to our development environment and can’t wait to hear your feedback. Let us know what you think!
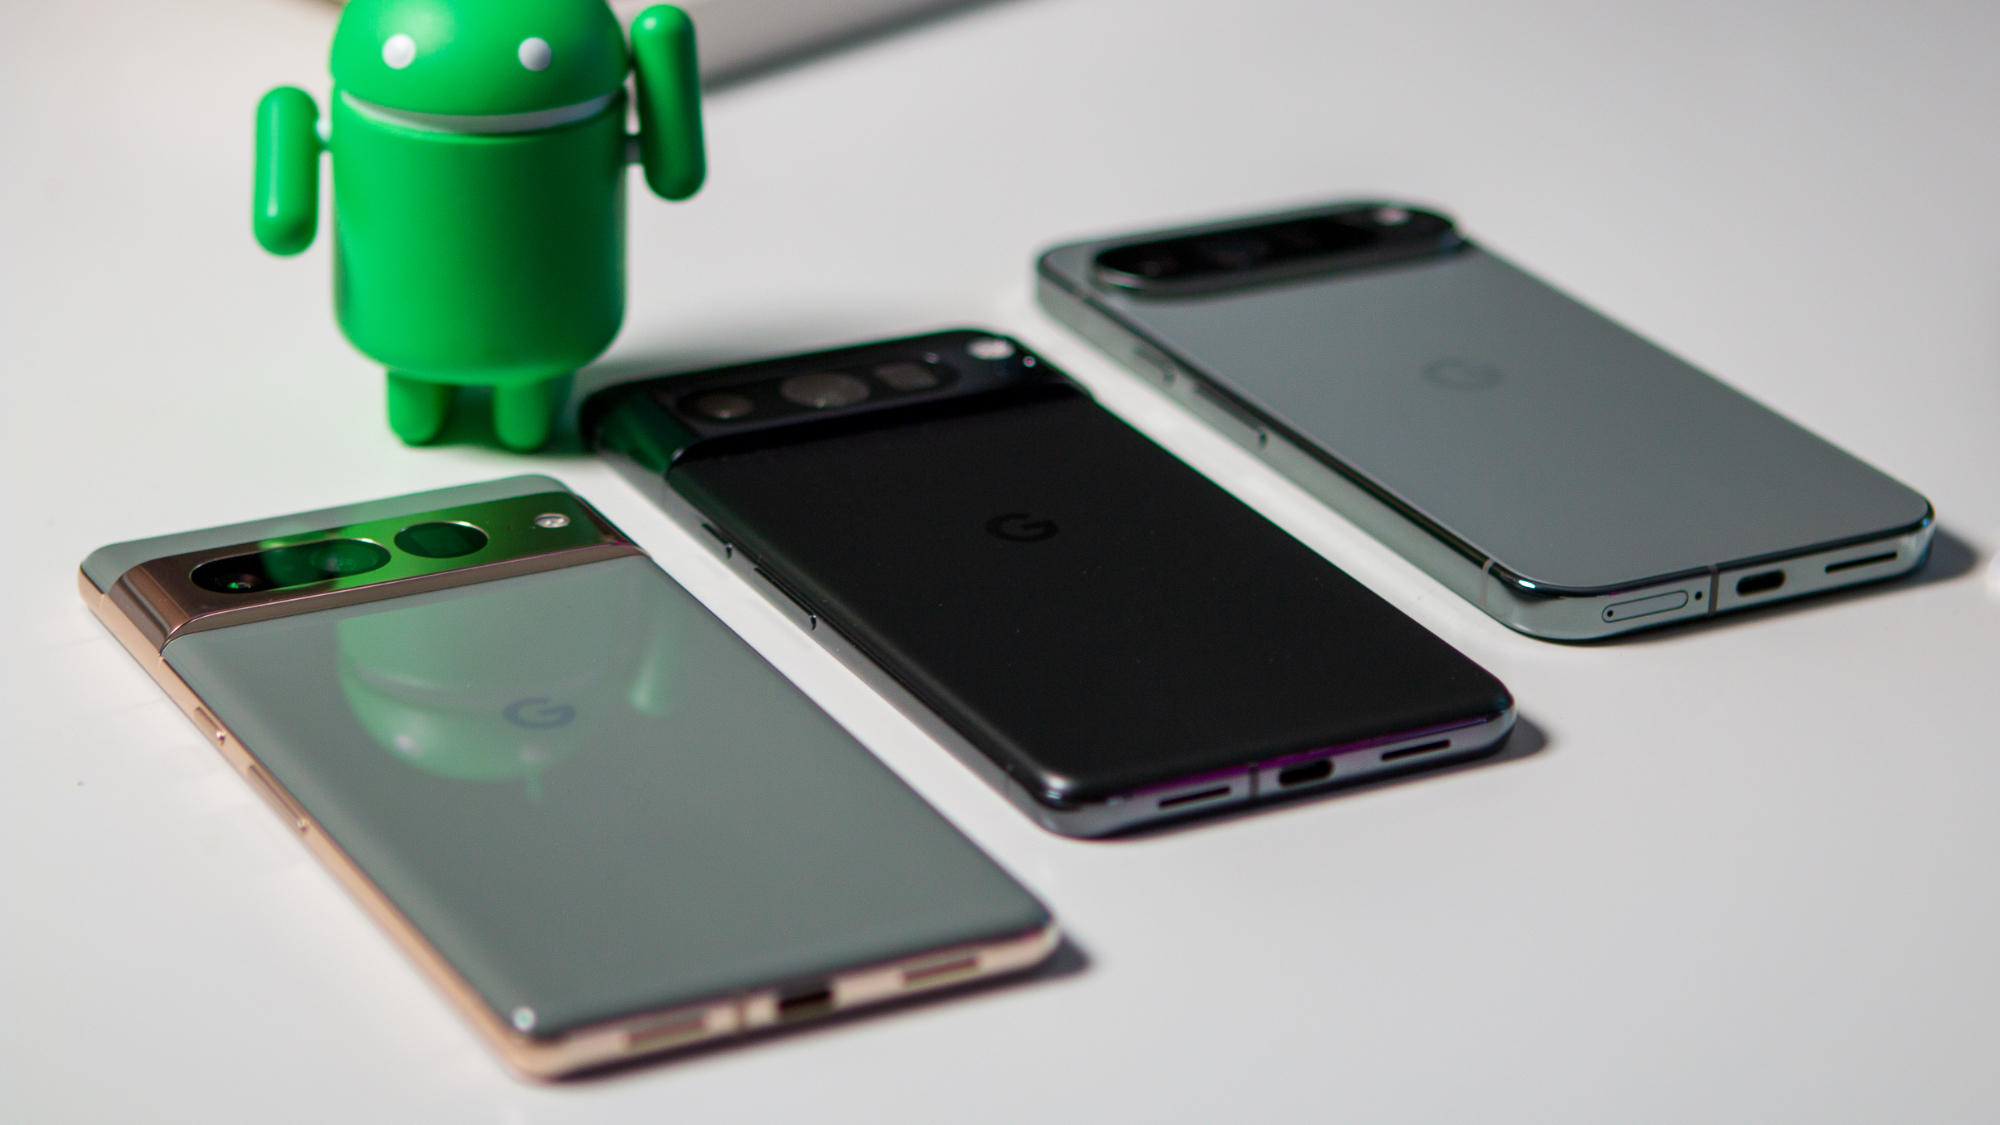
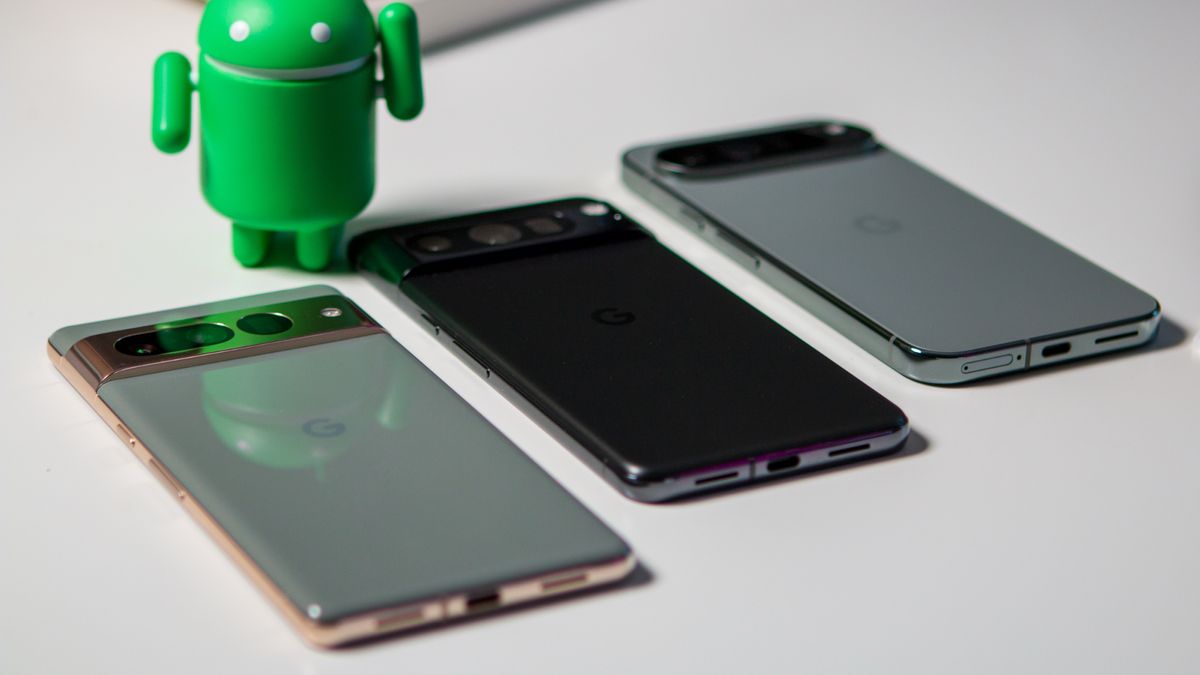
Google is changing its insurance partner for Preferred Care plans as of today, Feb. 24, and is adding a new payment option as part of the move. The company updated its official support page with the new insurance provider, as well as the one-time payment option that covers a Pixel phone, tablet, or watch for two years (via Android Authority). Previously, all Pixel devices had to be protected with Preferred Care via a subscription.
Google’s Preferred Care plans are a means of insuring a Pixel or Fitbit device, just like AppleCare Plus or Samsung Care. Starting today, there are two different ways of purchasing a Preferred Care plan. You can either insure the device for two years with a one-time payment, or choose a monthly subscription for up to 60 months of total coverage. In the event your screen is cracked, you’ll pay $29 for a repair or up to $129 for a replacement.
The new offering coincides with a notice that Google changed its insurance provider for Preferred Care: “If your device is shipped on or after February 24, 2025, your Service Contract Provider will be Asurion Warranty Protection Services, LLC, or one of its affiliates,” the company explains in the support document. “If your device is shipped prior to February 24, 2025, your Service Contract Provider will be Assurant.”
The only apparent consumer-facing change as part of the switch is the addition of the one-time payment option. Like the monthly plan, you can either add a plan during checkout at the Google Store or within 30 days of your purchase.
The prices for the two-year Preferred Care plans are as follows:
The above prices offer buyers a slight discount on Preferred Care compared to the cost of subscribing monthly for two years. Of course, the downside is that you can’t insure your Pixel device with Preferred Care beyond 24 months if you use the upfront option.
The U.K. government is pushing forward with plans to attract more AI companies to the region through changes to copyright law that would allow developers to train AI models on artists’ content on the internet — without permission or payment — unless creators proactively “opt out.” Not everyone is marching to the same beat, though.
On Monday, a group of 1,000 musicians released a “silent album,” protesting the planned changes. The album — titled “Is This What We Want?” — features tracks from Kate Bush, Imogen Heap, and contemporary classical composers Max Richter and Thomas Hewitt Jones, among others. It also features co-writing credits from hundreds more, including big names like Annie Lennox, Damon Albarn, Billy Ocean, The Clash, Mystery Jets, Yusuf / Cat Stevens, Riz Ahmed, Tori Amos, and Hans Zimmer.
But this is not Band Aid part 2. And it’s not a collection of music. Instead, the artists have put together recordings of empty studios and performance spaces — a symbolic representation of what they believe will be the impact of the planned copyright law changes.
“You can hear my cats moving around,” is how Hewitt Jones described his contribution to the album. “I have two cats in my studio who bother me all day when I’m working.”
To put an even more blunt point on it, the titles of the 12 tracks that make up the album spell out a message: “The British government must not legalize music theft to benefit AI companies.”
The album is just the latest move in the U.K. to bring attention to the issue of how copyright is being handled in AI training. Similar protests are underway in other markets, like the U.S., highlighting a global concern among artists.
Ed Newton-Rex, who organized the project, has simultaneously been leading a bigger campaign against AI training without licensing. A petition he started has now been signed by more than 47,000 writers, visual artists, actors, and others in the creative industries, with nearly 10,000 of them signing up in just the last five weeks since the U.K. government announced its big AI strategy.
Newton-Rex said he has also been “running a nonprofit in AI for the last year where we’ve been certifying companies that basically don’t scrape and train on great work without permission.”
Newton-Rex arrived at advocating for artists after having batted for both sides. Classically trained as a composer, he later built an AI-based music composition platform called Jukedeck that let people bypass using copyrighted works by creating their own. Its catchy pitch, where he rapped and riffed on the virtues of using AI to write music, won the TechCrunch Startup Battlefield competition in 2015. Jukedeck was eventually acquired by TikTok, where he worked for some time on music services.
After several years at other tech companies like Snap and Stability, Newton-Rex is back to considering how to build the future without burning the past. He’s contemplating that idea from a pretty interesting vantage point: He now lives in the Bay Area with wife Alice Newton-Rex, VP of product at WhatsApp.
The album release comes just ahead of the planned changes to copyright law in the U.K, which would force artists who do not want their work used for AI training purposes to proactively “opt out.”
Newton-Rex thinks this effectively creates a lose-lose situation for artists since there is no opt-out method in place, or any clear way of being able to track what specific material has been fed into any AI system.
“We know that opt-out schemes are just not taken up,” he said. “This is just going to give 90% [to] 95% of people’s work to AI companies. That’s without a doubt.”
The solution, say the artists, is to produce work in other markets where there might be better protections for it. Hewitt Jones — who threw a working keyboard into a harbor in Kent at an in-person protest not long ago (he fished it out, broken, afterwards) — said he’s considering markets like Switzerland for distributing his music in the future.
But the rock and hard place of a harbor in Kent are nothing compared to the Wild West of the internet.
“We’ve been told for decades to share our work online because it’s good for exposure. But now AI companies and, incredibly, governments are turning around and saying, ‘Well, you put that online for free …” Newton-Rex said. “So now artists are just stopping making and sharing their work. A number of artists have contacted me to say this is what they’re doing.”
The album will be posted widely on music platforms sometime Tuesday, the organizers said, and any donations or proceeds from playing it will go to the charity Help Musicians.
Nearly a month ahead of its scheduled release, physical copies of Assassin’s Creed Shadows have reportedly leaked, and people on social media are sharing images, gameplay clips, and other details about the game.
Copies of the game were reportedly being offered on Facebook Marketplace, and TheGamer has an image of one seller offering multiple copies for sale on online marketplace Mercari. Clips of gameplay have also been posted on Twitch and elsewhere, and while Ubisoft appears to be moving quickly to take them down, they’re not hard to find if you want to look. (To avoid potential spoilers, we will not be posting links.)
One person on Reddit noted that the leaked version being played is an “old build” that noticeably lacks some of the improvements that were promised when Assassin’s Creed Shadows was delayed out of 2024. That’s not terribly surprising given that the discs would have been produced weeks or months ago, and that weeks remain before full release. In the era of digital distribution, developers are typically working on games right up to the moment they go live, ensuring that everything is as it should be (or at least as close to it as possible) in a now-ubiquitous day one patch that’s meant to be available by the time you get your hands on that disc.
Regardless, this is a headache Ubisoft doesn’t need, especially given the long, bumpy road Assassin’s Creed Shadows has travelled so far. It’s been beset by problems pretty much from the moment it was announced in 2024: Aggrieved gamer outrage over the presence of the Black samurai Yasuke, a couple of self-inflicted injuries, and of course the last-minute delay that pushed it into February, and then March. In a way, this kind of last-minute mess almost feels inevitable: It’s been such a drawn-out rough go for Assassin’s Creed Shadows that one more stepped-on rake only makes sense.
Ubisoft hasn’t commented on the leak at this point, but I’ve reached out for more information and will update if I receive a reply.
I’m trying to import a user’s certificate from an SQLite database instead of using an actual file, but I’m encountering issues when attempting to use it with the pyhanko library for signing a PDF.
Here is my pdf-signer.py code, which implements a simple PDF signing process:
import sqlite3
from pyhanko.pdf_utils.incremental_writer import IncrementalPdfFileWriter
from pyhanko.sign import signers, timestamps
from pyhanko.sign.fields import SigSeedSubFilter
from pyhanko_certvalidator import ValidationContext
from pyhanko.keys import load_cert_from_pemder, load_certs_from_pemder_data, load_certs_from_pemder


with sqlite3.connect("pki.db") as conn:
    cursor = conn.cursor()
    cursor.execute("SELECT certificate FROM Users WHERE username=?", ('alice',))
    result = cursor.fetchone()


certificate_pem = result[0]
certificate_bytes = certificate_pem.encode("utf-8")
certs = list(load_certs_from_pemder_data(certificate_bytes))
user_cert = certs[0]

# Create the signer
signer = signers.SimpleSigner.load(
    cert_file=user_cert,
    key_file="key.pem"
)


root_cert = load_cert_from_pemder('rootca_cert.pem')

# FREE-TSA time stamper
timestamper = timestamps.HTTPTimeStamper(
    url="https://freetsa.org/tsr"
)
freetsa_root_cert = load_cert_from_pemder('tsa.crt')
signature_meta = signers.PdfSignatureMetadata(
    field_name="Signature", md_algorithm='sha256',
    subfilter=SigSeedSubFilter.PADES,
    validation_context=ValidationContext(
        allow_fetching=True,
        trust_roots=[root_cert, freetsa_root_cert]
    ),
    embed_validation_info=True,
    use_pades_lta=True
)
with open('input.pdf', 'rb') as inf:
    w = IncrementalPdfFileWriter(inf)
    with open('output.pdf', 'wb') as outf:
        signers.sign_pdf(
            w,
            signature_meta=signature_meta,
            signer=signer,
            timestamper=timestamper,
            output=outf
        )
The SimpleSigner.load() method expects a certificate file path (cert_file), but I’m trying to pass a certificate loaded from the database as a variable. How can I correctly load and use the in-memory certificate for signing?
I have tried loading data as bytes from the db with (load_certs_from_pemder_data(certificate_bytes)) and other methods but i keep getting the error : Could not load cryptographic material ,AttributeError: ‘NoneType’ object has no attribute ‘get_signature_mechanism_for_digest’