ID verification giant IDScan confirms data breach with more than 150 million driver’s licenses stolen


ID verification service IDScan has confirmed that a data breach involved the theft of driver’s licenses from its systems, a week after a report said the identity document checker had been breached during a year-long hack.

The company said in a website notice that hackers stole the driver’s licenses from the company’s cloud; the stolen information includes people’s full names and driver’s license numbers, along with identity numbers from other government-issued documents, such as passports.

The Louisiana-based firm is used by corporate customers from entertainment venues to cannabis dispensaries to check and verify the identity documents of their customers. The notice is the company’s first acknowledgement that it had been hacked. The company said last week that it was investigating an incident, but had not yet confirmed an intrusion.

IDScan said in its notice that it “received information” on or around September 1 about a claim of a hack, on the same day that independent cybersecurity journalist Brian Krebs first reported a data breach at IDScan. 

Krebs reported that he was alerted to a website on the dark web that allowed anyone to search the driver’s license information of over 150 million people living in the United States and Canada, including accessing their photos. Krebs verified the authenticity of the data by examining his own record. The database also contained high-profile individuals, including the U.S. Secretary of Defense Pete Hegseth, and a security researcher who also verified his data for Krebs’ report.

The Pentagon told TechCrunch last week that it was aware of the suspected breach, and a spokesperson for the FBI said it was also investigating the incident.

IDScan said on its website its investigation was ongoing. The company’s statement said that, “though full access to the information required payment” — likely referring to a demand for money made by the hackers to access the full cache of stolen data — the company was providing notice on its website to notify potentially affected individuals. IDScan has not said how many individuals are affected but notes on its website that it holds over 150 million driver’s license records.

IDScan did not respond to TechCrunch’s request for comment about the incident, such as whether the hackers contacted the company with a ransom demand not to release the data.

When you purchase through links in our articles, we may earn a small commission. This doesn’t affect our editorial independence.

NVIDIA and CrowdStrike Strengthen Agentic Cybersecurity Frontier


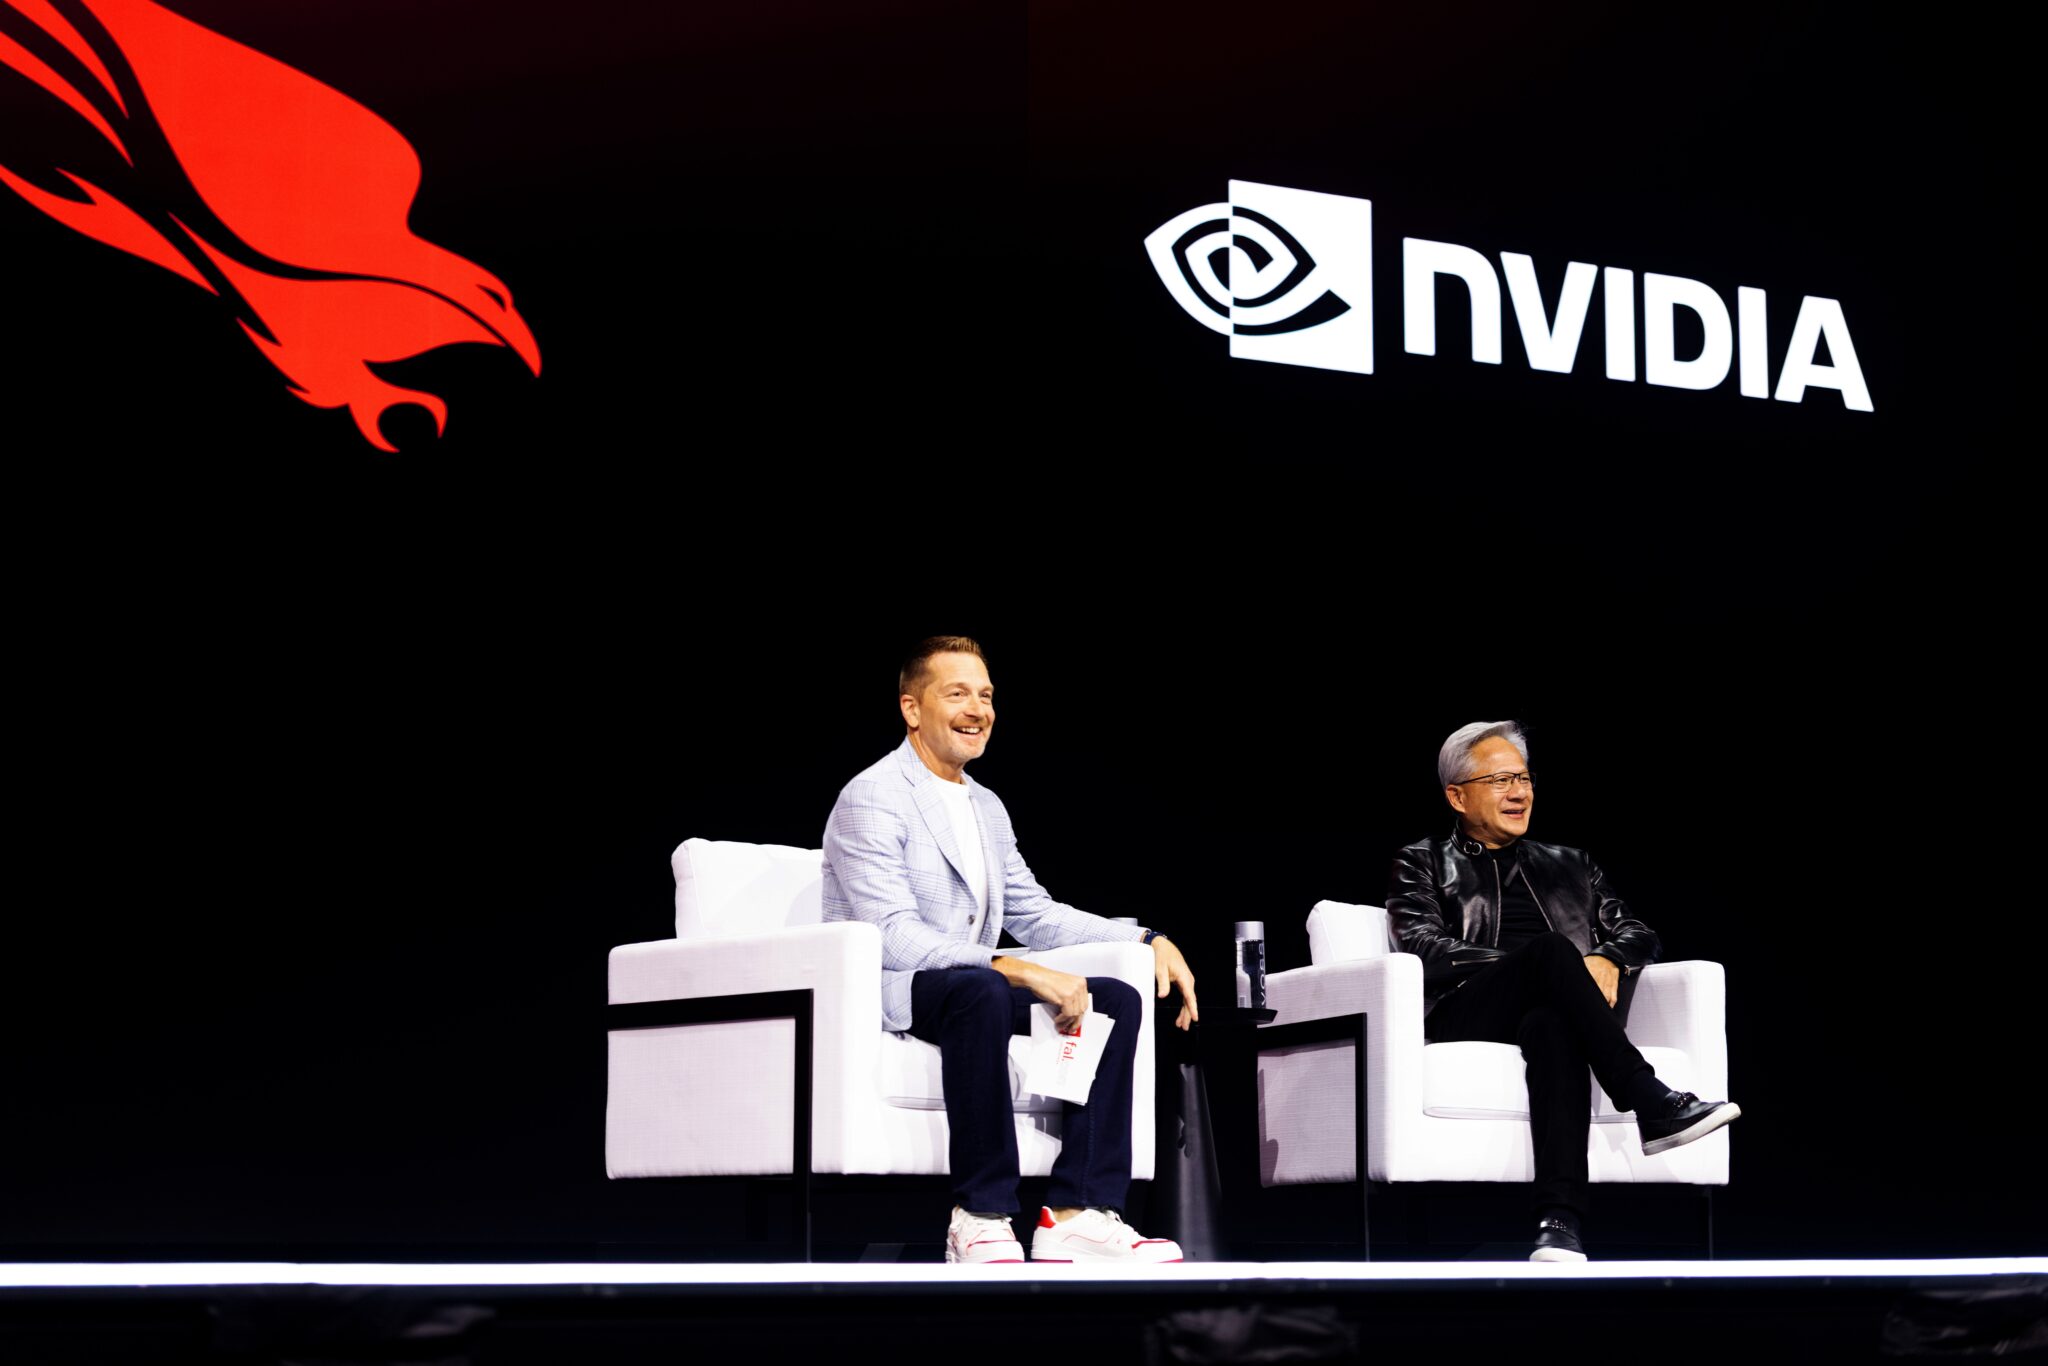
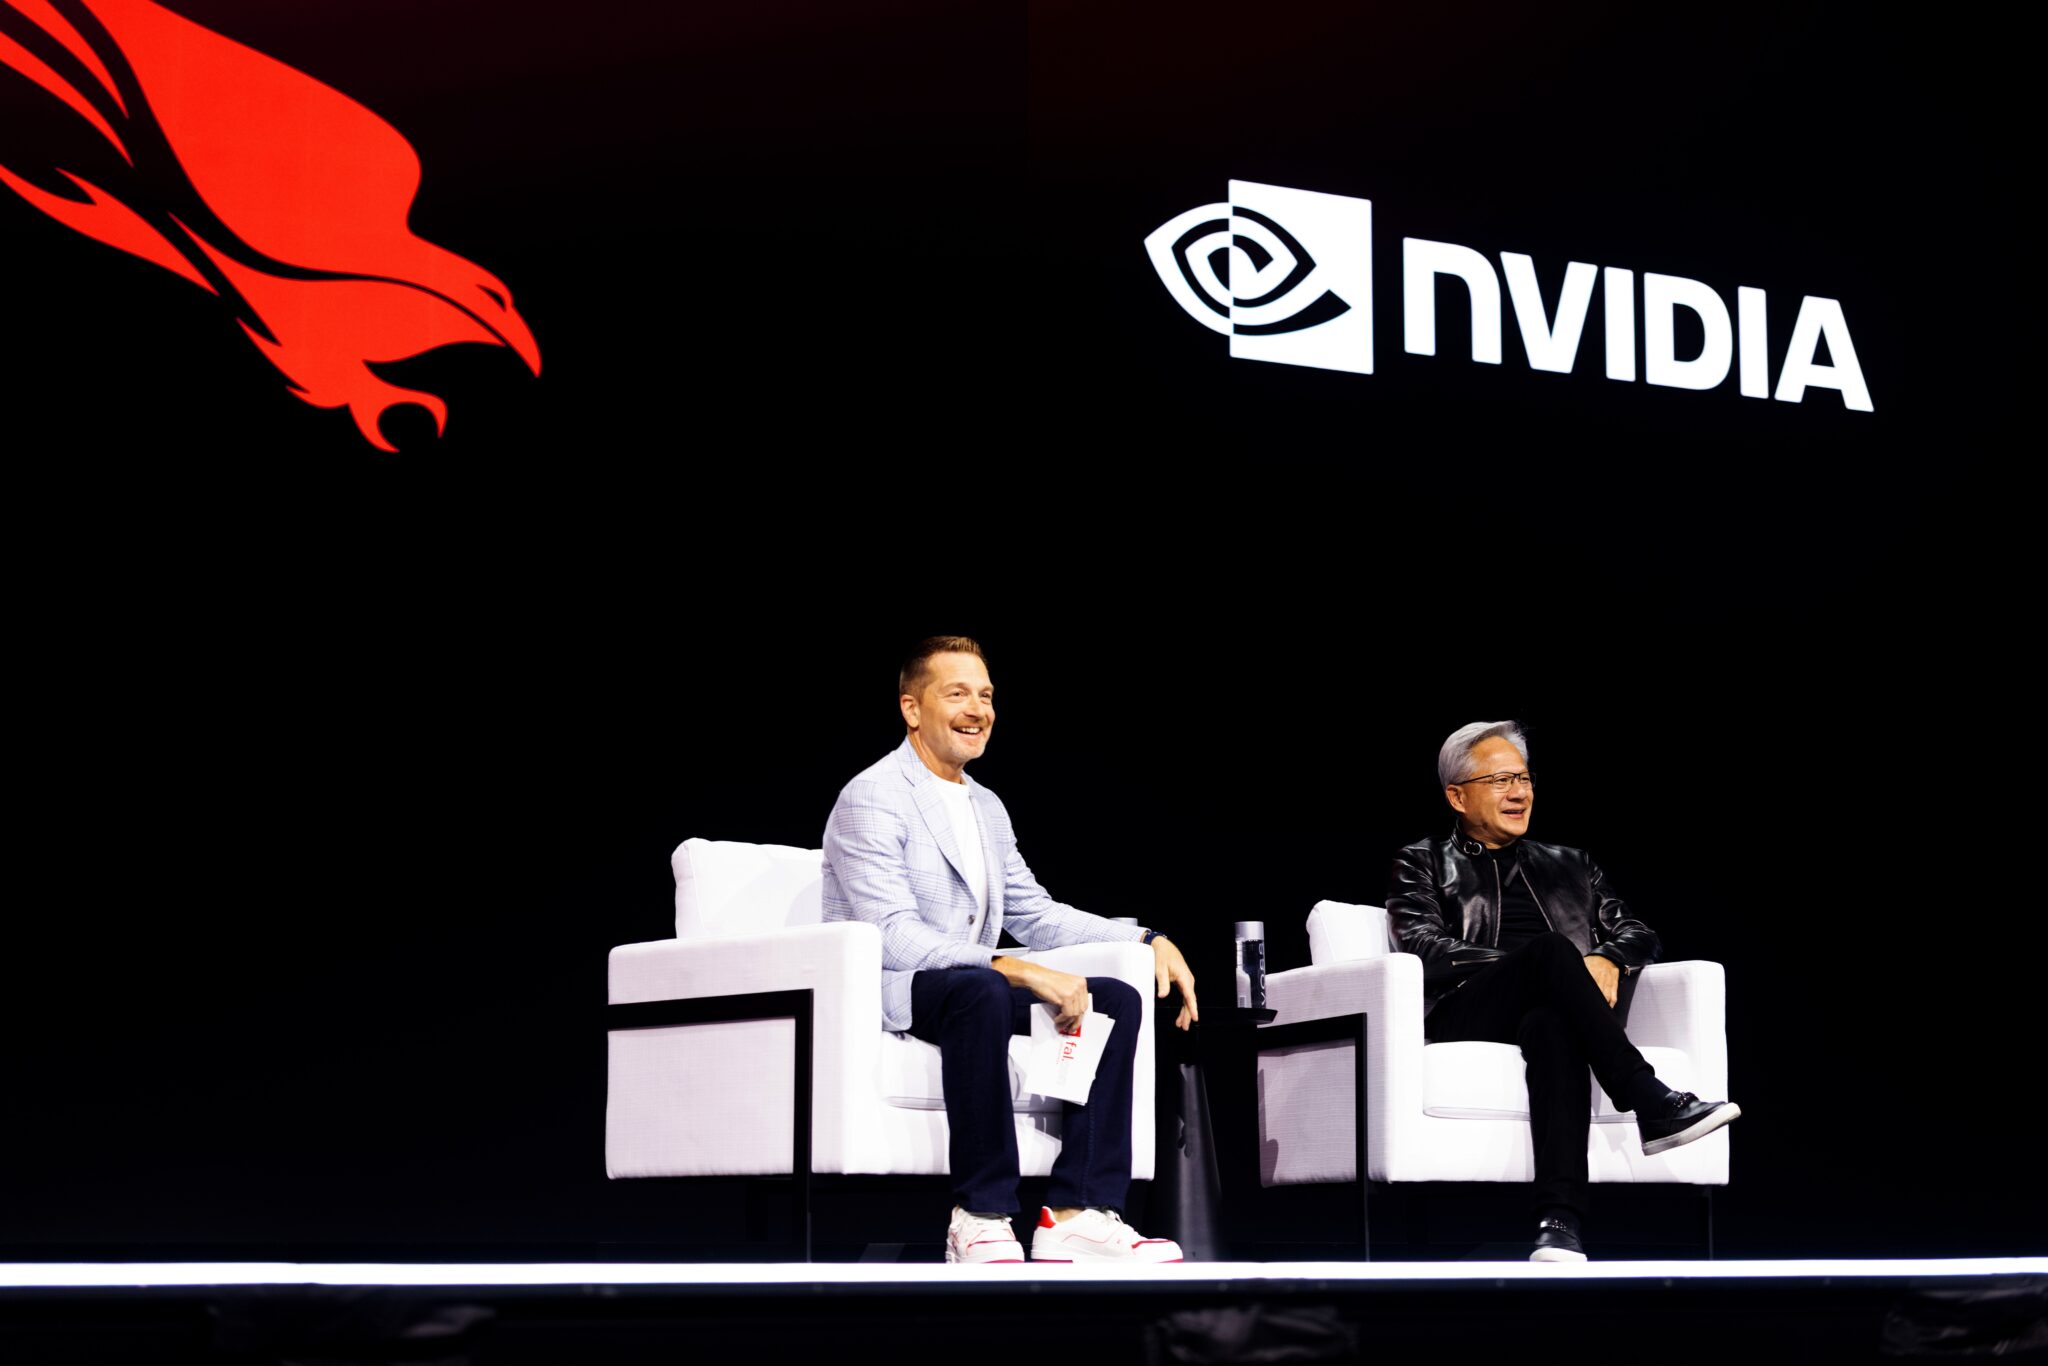
“We’re at an inflection point in cybersecurity,” Jensen Huang told a sold-out crowd at CrowdStrike’s Fal.Con 2026 in Las Vegas Tuesday. Attacks are now automated. Defense has to be, too. 

The NVIDIA founder and CEO joined CrowdStrike CEO and founder George Kurtz to announce CrowdStrike SafeMind, its agentic cybersecurity system developed by the CrowdStrike Cyber Superintelligence Lab.

“This is the beginning of a new age of cybersecurity,” Huang told the crowd of 10,000 security professionals. “On the one hand, the adversaries are going to be more armed than ever. On the other hand, all of you are going to be more armed than ever.” 

SafeMind combines CrowdStrike’s purpose-built, beyond frontier-capable models and customized agentic harnesses, with defensive models built on NVIDIA Nemotron, in a continuous coevolution loop where offense and defense repeatedly challenge and improve each other. 

CrowdStrike also announced CrowdStrike Falcon IQ to operationalize Project QuiltWorks through agentic workload automation and expanded its CrowdStrike Guardian AI safety solution.

“We have asymmetric advantages because we have a large community of cybersecurity experts who want to work with each other and keep the world safe,” Huang told the crowd. 

CrowdStrike’s annual conference drew security leaders from financial services, healthcare, the public sector and critical infrastructure.

“The real gap that I saw was that the attackers had frontier AI, and the defenders didn’t,” Kurtz told them. “And that changes now.”

SafeMind

CrowdStrike built SafeMind’s defensive model using NVIDIA Nemotron open models, post-trained with CrowdStrike’s cyber experience and threat data. The SafeMind models are paired with proprietary cybersecurity harnesses optimized to work as an agentic stack.

The result ships natively in the CrowdStrike Falcon platform as SafeMind, CrowdStrike’s agentic cybersecurity system. SafeMind brings offensive and defensive AI together in a continuous coevolution loop, where each side adapts to and strengthens the other. This process continuously hardens the security of the customer environment until attacks are unsuccessful.

“Your decade and a half of security data that we can train on — we can take a frontier model and make it essentially a super AGI that is incredibly good at cybersecurity,” Huang told Kurtz.

“Together with NVIDIA, we built cybersecurity’s first complete agentic system for cybersecurity, including the first frontier models and harness purpose-built for defenders,” Kurtz said. “This isn’t a copilot baked into someone else’s intelligence. It’s not a chatbot with a security skin. It is a frontier-class model built and trained by CrowdStrike on our data in partnership with NVIDIA.”

NVIDIA Nemotron 3 Ultra orchestrates the defensive agent harness. A fine-tuned Nemotron 3 Super powers SafeMind’s rule-generation sub-agent. 

By post-training Nemotron with CrowdStrike data, CrowdStrike internal evaluations showed that the Blue Solano model — based on Nemotron 3 Super — delivered higher accuracy rates than leading frontier models at 99% lower cost. 

While SafeMind can operate as a complete system, the models can be used independently to empower defenders to stay ahead of the adversary. Security experts can also pair their own models with CrowdStrike’s custom harnesses, giving customers the flexibility to use the right models and capabilities for their environment.

“The harness is essentially the exoskeleton of the large language model,” Huang said. “The large language model is the brain. The exoskeleton turns it into an agent — and this exoskeleton doesn’t have to be the same shape and capability for every domain.”

When AI Is the Defense

AI-enabled attacks rose 89% in the past year, and the fastest eCrime breakout time has reached 27 seconds, according to CrowdStrike. Human-speed response isn’t defense. It’s documentation.

“There are many applications in the world where you must have the ability to fine-tune, to post-train — to create an AI that is super good at a particular domain,” Huang said. “Nemotron was created for precisely that. Completely free. Incredibly fast. You have the ability to have an asymmetric advantage against whatever comes your way.”

With open Nemotron as the base, CrowdStrike’s security teams post-trained on their own threat data without sending it to an outside provider, and customized the AI to their environment. 

That’s not possible with a closed frontier model, and in security, the ability to inspect what’s defending matters. 

Red vs. Blue

NVIDIA announced its work testing the CrowdStrike SafeMind models and harnesses in a high-fidelity cyber agent environment running as a simulation of the NVIDIA network. 

The testing runs SafeMind in an offensive-defensive loop for adversarial coevolution. An offensive red-team agent finds the exploit, a blue-team defensive agent closes it and the findings become actionable detections to block attacks. 

The red-agent harness runs Recon, Assault and Compromise sub-agents executing attack paths inside the cyber agent environment. The blue-agent harness monitors via Falcon sensors, generates detection candidates, validates them and promotes them. 

CrowdStrike built the test environment with NVIDIA: a digital twin of NVIDIA’s own accelerated computing infrastructure, validated against NVIDIA’s real threat landscape.

“The basic framework of SafeMind — an adversarial model acting on a digital twin of the environment, with a defender model in a continuous cat-and-mouse loop, eventually learning how to secure itself — this basic framework applies to robotics, edge computing, enterprise computing and just about everything,” Huang said.

CrowdStrike also announced Falcon IQ. NVIDIA Nemotron models help to power the agentic engine at the heart of Charlotte AI AgentWorks, CrowdStrike’s no-code agent development platform where Falcon IQ runs. 

Falcon IQ uses more than 50 agents working together as a unified agentic workforce to automate the most time-intensive workflows in assessment, prioritization and remediation. 

Partners use Falcon IQ to deliver customized findings, recommendations and executive outputs to customers. Charlotte AI AgentWorks enables every Falcon user to build their own agentic security workforce.

The Full Stack

CrowdStrike has thousands of customer organizations generating trillions of daily security events. 

With NVIDIA’s full-stack accelerated computing platform, the collaboration runs from the chips up through the models to the harnesses acting on what those models find. For Kurtz, that’s the point. 

“The crowd in CrowdStrike,” Kurtz added, “is the asymmetry that puts the defenders in a unique position to defeat the adversary.”
How to tell if your AI platforms’ accounts have been hacked


Just like any other online service, hackers can target and break into your accounts on popular AI platforms such as ChatGPT, Claude, and Perplexity. 

TechCrunch has created a comprehensive guide to help you protect yourself if you suspect someone has broken into your account on one of the internet’s most popular platforms, social networks, or messaging apps. Now, we’re here to show you how to check whether your accounts on AI platforms have been hacked.

As usual, we recommend using unique passwords stored in a password manager, and turning on multi-factor authentication (MFA), so that even if someone steals your password, they won’t be able to log in without that second piece of information. 

ChatGPT and Perplexity offer MFA. Claude doesn’t, because instead of asking for a password, Anthropic’s AI chatbot sends a login link to your email address.

All three of these AI platforms offer similar ways to check if there’s a suspicious device logged into your account. Here’s exactly how each platform works.  

ChatGPT

To find out if someone has broken into your ChatGPT account, open it on your computer’s browser, click on your username in the bottom left corner, go to “Settings,” then “Security and Login,” and finally click on “Active Sessions.” 

You will see where you are logged into your ChatGPT account. If you see any device you don’t recognize, you can log out of that single device. You can also click on “Log out all.”

Image Credits:Screenshot/TechCrunch /

At this point, if you want to change your password, you need to log out of your account. 

Then, on ChatGPT’s website, click “Log in” located in the bottom-left corner, enter your email address, click on “Forgot password,” and then “Continue.”  

ChatGPT will then send you an email containing a six-digit code. Enter the code on the ChatGPT login page, click “Continue,” and then enter a new password. 

You can also click “reset your password” in the email you received to see the official instructions on how to do that. 

Claude

For Claude, open it in your computer’s browser, click on your username in the bottom-left corner, then “Settings,” and click on “Account.” That’s where you will see your “Active sessions.” 

If you don’t recognize one of them, hover over it, click on the three vertical dots that appear on the right, and click “Log out” or “Terminate.”

Image Credits:Screenshot/TechCrunch /

If you want, you can click on “Log out of all devices.” 

At that point, you’ll be able to log back into your account using your email address. You will receive an email with a link to log in. Claude does not allow you to use passwords at all, so there’s no password to change.

Perplexity

In the case of Perplexity, the AI-powered search engine does not show you where you are logged in. 

So if you’re worried someone may have broken into your account, go to Perplexity in your browser and click your username in the bottom-left corner, then “All settings.” Finally, click on “Sign out of all sessions,” and then “Confirm.”

Image Credits:Screenshot/TechCrunch /

At that point, you can log back in by entering your email address. You will then receive an email with a unique six-digit code. Enter the code on the website to log in, or click on the “Sign in” button in the email to log in directly. 

When you purchase through links in our articles, we may earn a small commission. This doesn’t affect our editorial independence.

Trump Admin Lets the Cyber Pirates Loose


The White House will give cybersecurity firms permission to conduct “offensive cyber operations aimed at disrupting criminal organizations,” Bloomberg reported on Thursday.

Trump’s administration has spent months waffling on the idea, which is substantially similar to the centuries-old practice of issuing letters of marque. That’s a type of document from the Age of Sail which extended official protections to private vessels to attack pirates and enemy vessels, a legal (depending on who you ask) and regulated form of piracy known as privateering.

A fact sheet on the National Security Presidential Memorandum (NSPM) states the interagency National Coordination Center will split oversight of the program between two executive directors from the departments of Homeland Security and Justice. The order encourages security firms to voluntarily enter intelligence-sharing agreements with government agencies from the local to federal level, and propose and help carry out “cyber operations that address those threats.”

Currently, most “offensive” cyber operations are undertaken by profit-minded criminals, military units like U.S. Cyber Command, or intelligence agencies and their various proxies. That’s because they’re potentially both illegal and interpretable as acts of aggression, not to mention that they can invite revenge. Private companies, fearing liability issues, have tended to draw the line at what’s called active defense, a somewhat ambiguous term that covers tactics like seeking court orders to take down hacker infrastructure or setting up honeypots.

The NSPM fact sheet states the program’s overseers will develop “rigorous procedures for the review and conduct” of offensive cyber operations. Curiously, cybersecurity firms which want to participate will be required to hold $1 million in bond/escrow, which may be forfeited in the case of a contract violation.

The idea of hacking back isn’t new. In 2019, CyberScoop noted it had attracted the moniker of “worst idea in cybersecurity” among cyber policy types, with experts pointing out that it is hard to accurately identify perpetrators and could result in damaging crossfire between governments and private actors. Even Trump’s own officials have, at times, denied even considering it.

In March 2026, CyberScoop reported then-Office of the National Cyber Director senior adviser Thomas Lind had shot down growing speculation the White House would embrace private offensive operations, stating at a conference the administration is “not interested in fighting pirates with pirates.” National Cyber Director Sean Cairncross told attendees at a security summit in D.C. around the same time that private offensive cyber operations are “not what we’re talking about” when asking for more help from industry.

There’s good reason for hesitation. Obfuscation is an ubiquitous element of cyber attacks, as attackers go to great lengths to prevent detection (at least until the commencement of the attack) and are happy to exploit information asymmetry in any way possible. Threat actors are also often less coherent entities than overlapping, temporary associations between cybercriminals, further complicated by the emergence of a huge cybercrime-as-a-service economy and the formation of supergroups like “Scattered Lapsus$ Hunters”.

Then there’s the possibility of tit-for-tat retaliatory cycles such as those witnessed in the ongoing physical and cyber war between Ukraine and Russia. It’s worth noting that Trump’s White House has a grudge against the Cybersecurity and Infrastructure Security Agency (CISA) for not taking his side while he was trying to overturn the results of the 2020 presidential election. Back in office, his White House has aggressively slashed CISA’s budget and personnel—keep in mind this is the agency that is supposed to help coordinate threat intel sharing and defenses in the event something in cyberspace goes hot.

Canadian spy agency says it hacked drug traffickers, extremists and a ransomware gang last year


Offering a rare glimpse at the priorities of a top spy organization, Canada’s Communications Security Establishment said it conducted a handful of state-authorized hacks last year in order to disrupt the operations of drug traffickers, violent extremists, and a ransomware gang.

The disclosures in the Canadian intelligence agency’s annual report underscore some of the main national security threats that face Canada and its closest allies: ranging from the import of illegal drugs to cyberattacks. The spy agency, CSE, is tasked with collecting foreign intelligence, defending government systems, and disrupting online adversaries.

Published last week, the report says the CSE last year carried out three foreign “active cyber operations” — the term agency uses to describe its cyberattacks on overseas operations that threaten Canadian national security and public safety.

One of the operations, per the report, targeted cybercriminals outside of Canada who were brokering the sale of chemicals used to create the synthetic opioid, fentanyl. The CSE collected intelligence on the brokers, then conducted an operation that “disrupted and diminished their ability to operate,” the report said.

Another active operation involved the collection of signals intelligence — data produced from electronics and internet-connected devices — on an overseas extremist group that was spreading violent ideology and recruiting members, including in Canada.

The report said the agency analyzed the group’s organization, reach, and potential vulnerabilities to conduct an operation that “successfully undermined the group’s credibility and limited their ability to radicalize and recruit new members.”

Another operation involved disrupting a ransomware-as-a-service operation that let hackers rent access to a ransomware gang’s infrastructure to launch destructive extortion attacks. The CSE said its signals intelligence unit identified how the gang worked against the healthcare, transportation, and business sectors in Canada, then used an active cyber operation that “rendered the group’s infrastructure inoperable.” The operation also deleted much of the data on the gang’s servers.

The agency said it undertook concurrent “technical disruptions” against 10 of the most significant ransomware gangs targeting Canada to “make parts of their infrastructure unusable.”

The report did not say where the hackers, extremists or the ransomware gang were located, or the specifics of the operations that the CSE used to target them. It’s not uncommon for spy agencies to conduct cyberattacks against their adversaries, but such operations are seldom disclosed or detailed to protect the methods and techniques used.

Fort Meade, Maryland-based Cyber Command, which conducts cyber operations for the U.S. government, regularly carries out “hunt forward” operations that involve sending cyber teams to allied nations to secure their networks and disrupt cyber operations launched by adversaries. The number of U.S.-led hunt forward operations have risen from a few handful during 2018 to more than two dozen during 2025.

Canada’s CSE said it also carried out one defensive cyber operation during the year to target a phishing campaign aimed at Canadian federal government institutions and other important systems. The agency said it disrupted the group’s infrastructure and “degraded their ability” to target Canadians.

When you purchase through links in our articles, we may earn a small commission. This doesn’t affect our editorial independence.

Politician who investigated spyware abuses had his phone hacked with Pegasus spyware


Security researchers have confirmed that a European politician had his phone hacked with the Pegasus spyware while serving on an investigatory committee probing abuses of the notorious surveillance tool. This has reigniting fresh controversy over governments abusing spyware to collect information about their critics.

The researchers at the University of Toronto’s digital rights unit The Citizen Lab say the confirmed phone hacking of Greek journalist and former politician Stelios Kouloglou during 2022 and 2023 marks the first time that a member of the European Parliament’s PEGA committee, tasked with investigating phone spyware attacks by European governments, has been publicly identified as a victim of spyware.

Kouloglou told TechCrunch in a phone call that the deliberate compromise of his phone was “reckless.” One serving European lawmaker described the hacking of Kouloglou’s phone as a “direct attack on the rule of law,” and called on the European Commission to take concrete action by imposing strict limits on the use of spyware across the 27 member-state bloc.

While spyware attacks on lawmakers are rare, the timing and targeting of a committee investigator by way of the very spyware under his investigation suggests an intense focus on the committee’s inner workings ahead of a widely anticipated report detailing its findings. The hacks open fresh questions about how governments use spyware ostensibly needed for identifying serious crime, but then caught spying on the communications of journalists, lawmakers, and critics.

Citizen Lab’s researchers did not attribute the phone hacking to a specific country, but said that the government customer used the same Pegasus-loaded email address that was used in a previous campaign that hacked into the phones of journalists across Europe. The customer’s identity is not known, but the reuse of the same attacking email address implies that the customer had NSO Group’s authorization to use its Pegasus spyware to snoop on phones across multiple countries in Europe.

A spokesperson for the European Commission did not respond to TechCrunch’s request for comment. NSO Group also did not respond to a request for comment about the Citizen Lab report prior to publication.

In its report out Friday, Citizen Lab said Kouloglou was hacked in October 2022 and at least twice during March 2023 using an exploit that compromised a security vulnerability in Apple’s iPhone software. This vulnerability had been patched but the fix was not yet installed on Kouloglou’s phone. The exploit was a “zero-click” bug, meaning the spyware broke in and stole his data without needing any interaction on his part.

The bug abused a previously discovered flaw in Apple’s smart home software used in iPhones. It allowed the spyware to grab private data from Kouloglou’s phone without his knowledge, such as his text messages and other correspondence, location data, and photos.

The timing of the October 2022 hack coincides with intense discussions over email and text message throughout October and November 2022, ahead of the delivery of a first draft describing spyware abuses focusing in Cyprus, Greece, Hungary, Poland, and Spain. 

The hack also lines up at the exact time that Kouloglou was in the hospital at the time for a pre-scheduled surgery, which may have allowed the spyware operators to listen in to ambient audio discussing his healthcare or other conversations he had with visitors at the time.

Months later on March 6 and 7, Citizen Lab said Kouloglou’s phone was hacked again by the same Pegasus operator while Kouloglou traveled from Athens to Brussels, during a period of committee hearings and months prior to the committee finalizing and adopting their written draft report.

In a call, Kouloglou told TechCrunch that he didn’t know why he was specifically targeted but that he believes it was due to his work on the European Parliament’s committee investigating Pegasus abuses.

He described anger when he learned that his phone had been hacked. 

“You realize that all of your personal data [was taken] — not all the professional exchanges or messages with ministers — but also the very private things, like the happy moments and the sad moments,” he told TechCrunch.

Kouloglou said he plans to sue NSO Group, the Israeli-headquartered spyware maker. NSO remains largely banned from use in the United States following a Biden-era executive order that outlawed the government’s use of spyware that could violate people’s human rights. 

Last year, the spyware maker confirmed an unnamed American investment group funneled tens of millions of dollars into the company, likely as part of an effort to rehabilitate NSO’s beleaguered brand associated with enabling human rights abuses.

Kouloglou said he was going public with his story “for democracy, human rights, and the fight against corruption.”

“Corruption concerns everybody,” he said.

When you purchase through links in our articles, we may earn a small commission. This doesn’t affect our editorial independence.

Password manager maker LastPass says hackers stole customer support case data during Klue breach


Password manager maker LastPass is notifying customers that their personal information and customer support case records were stolen during a recent hack at one of its technology partners, marking the company’s latest data breach in recent years.

In an email shared with TechCrunch from an affected customer, LastPass said the breach occurred at market research firm Klue, and not its own systems. However, hackers abused their access to obtain reams of data about LastPass customers.

LastPass is the latest in a growing list of cybersecurity companies that have reported data thefts as a result of the breach at Klue, which the company disclosed last week. Several other affected companies include HackerOne, Recorded Future, and Tanium.

In a blog post that shared information about the incident, LastPass said the hackers took customers’ names, phone numbers, email addresses, physical addresses, as well as customer support case data and sales-related data.

LastPass said the company’s own infrastructure was unaffected, including customers’ password vaults.

It’s not yet known what was in the contents of customer support tickets, although they likely contain fragments of potentially private or sensitive information. Customers typically contact customer service when they are having a billing issue or need assistance in gaining access to their accounts. Past incidents involving customer support tickets have included credentials and government-issued identity documents.

Spokespeople for LastPass did not immediately respond to TechCrunch’s request for comment, or questions about the incident, including how many customers are affected by the incident. 

LastPass has more than 33 million users and around 1.6 million paying customers as of 2024, according to its website.

LastPass previously experienced a data breach in 2022, in which hackers stole the company’s entire store of customer password vaults, which are used to store their sensitive credentials, such as passwords, tokens, and other personal and credit card numbers.

While the vaults were encrypted with master passwords only known to the customer, the breach allowed hackers to brute-force and crack the vaults offline with the weakest master passwords, and subsequently access the secrets inside. Several crypto thefts were later linked to the LastPass breach, after hackers were suspected of stealing the victim’s wallet keys by cracking their password vault.

Klue CEO Jason Smith said in a blog post that the company identified hackers in its systems on June 12. A hacking and extortion group called Icarus took credit for the breach, and have publicly threatened to release the stolen data if a ransom isn’t paid.

Smith has not responded to TechCrunch’s emails about the incident, including how many customers are affected or if the company has been in contact with the hackers.

When you purchase through links in our articles, we may earn a small commission. This doesn’t affect our editorial independence.

South Korea hits Coupang with $400M+ fine for data breach that affected millions


South Korean authorities have imposed a record-breaking fine of $624 billion won (over $400 million) on retail giant Coupang after a data breach last year compromised the personal data of more than 34 million customers.

Seoul’s Personal Information Protection Commission issued the maximum penalty on Thursday following discovery of the breach in December 2025. The retail giant, which is headquartered in the U.S. but popular in South Korea and likened to the “Amazon of Asia,” had said the months-long data breach allowed a former employee to obtain names, email and shipping addresses, phone numbers and order histories of about two-thirds of South Korea’s population.

Coupang told BBC News that it plans to challenge the regulator’s decision. The fine represents a rare case of a financial penalty issued against a U.S.-based firm. Korean lawmakers have accused some of their American counterparts of imposing political pressure after reports that U.S. representatives were linking the data breach with U.S.-South Korean bilateral ties in response to the case against Coupang’s executives.

U.S. companies rarely face financial sanctions or criminal prosecution for data breaches as a result of lacking laws and enforcement powers.

Booking.com confirms hackers accessed customers’ data


Booking.com confirmed Monday that hackers may have accessed customers’ personal data, including names, emails, physical addresses, phone numbers, and booking details. The global travel and hotel reservation giant notified customers this past week of the breach, according to several online posts. 

“We’re writing to inform you that unauthorized third parties may have been able to access certain booking information associated with your reservation,” read the notificaiton to customers, according to one user’s post on Reddit. Several other Reddit users replying to the post said they received the same notification. The message from the company included the aforementioned types of compromised data, as well as “anything that you may have shared with the accommodation.” 

The user who posted the notification on Reddit told TechCrunch that they received a phishing message via WhatsApp two weeks ago that included “booking details and personal information.” That suggests hackers are leveraging the stolen information to target Booking.com customers. 

Booking.com spokesperson Courtney Camp told TechCrunch that the company “noticed some suspicious activity involving unauthorized third parties being able to access some of our guests’ booking information. Upon discovering the activity, we took action to contain the issue. We have updated the PIN number for these reservations and informed our guests.” 

The spokesperson declined to answer TechCrunch’s specific questions, including how many customers were affected by this incident and then notified. 

The company told The Guardian that “financial information was not accessed”.

In 2024, TechCrunch reported that hackers had infected several hotels’ computers with consumer-grade spyware, or stalkerware. In one case, a victim was logged into their Booking.com administration portal when the PcTattleTale stalkerware took a screenshot of their screen. 

Techcrunch event

San Francisco, CA
|
October 13-15, 2026

According to the company’s website, 6.8 billion customers have booked hotel rooms and homes since 2010.

Iran-Linked Hackers Are Sabotaging US Energy and Water Infrastructure


As US President Donald Trump threatens wholesale demolition of Iran’s infrastructure in the midst of an escalating war, Iran now appears to have already reciprocated with its own form of infrastructure sabotage: A hacking campaign hitting industrial control systems across the United States, including energy and water utilities, that US agencies say has had disruptive and costly effects.

In a joint advisory published Tuesday, a group of US agencies including the FBI, the National Security Agency, the Department of Energy, and the Cybersecurity and Infrastructure Security Agency warned that a group of hackers affiliated with the Iranian government has targeted industrial control devices used in a series of critical infrastructure targets including in the energy sector, water and wastewater utilities, and unspecified “government facilities.” According to the agencies, the hackers have targeted programmable logic controllers (PLCs)—a type of device designed to allow digital control of physical machinery—in those facilities, including those sold by industrial tech firm Rockwell Automation, with the apparent intention of sabotaging their systems.

By compromising those PLCs, the advisory warns, the hackers sought to change information on the displays of industrial control systems, which can in some scenarios cause system downtime, damage, or even dangerous conditions. “In a few cases, this activity has resulted in operational disruption and financial loss,” it reads.

When WIRED reached out to Rockwell Automation, a company spokesperson responded in a statement that it “takes seriously the security of its products and solutions and has been closely coordinating with government agencies in connection with” Tuesday’s advisory, and pointed to documents it has published for customers on how to better secure their PLCs.

Though the advisory doesn’t specify a particular group responsible for the hacking campaign, it notes that the attacks are similar to those carried out in by the Iran-linked group known as CyberAv3ngers, or the Shahid Kaveh Group, starting in late 2023. That team of hackers, believed to work in the service of the Iranian Revolutionary Guard Corps, inflicted several waves of attacks against Israeli and US targets in recent years, including gaining access to more than a hundred devices sold by industrial control system technology firm Unitronics and most commonly used in water and wastewater utilities.

This is a developing story, please check back for updates.