Trump, teen suicides, and other controversies ‘The Social Reckoning’ misses


Aaron Sorkin, famed writer of The West Wing and Academy Award-winning The Social Network, is notoriously verbose. He has a reputation for linguistic flairs that some find awkward, and many find deeply compelling. 

But in The Social Reckoning, a follow-up to the 2010 tale of Facebook’s founding, he is uncharacteristically sparing. 

Yes, Sorkin — who wrote and directed the new movie — crams the script with one-liners and existential metaphors, random pop culture references, and cries for change, but it’s what he leaves out that viewers should pay attention to. 

What ‘The Social Reckoning’ omits

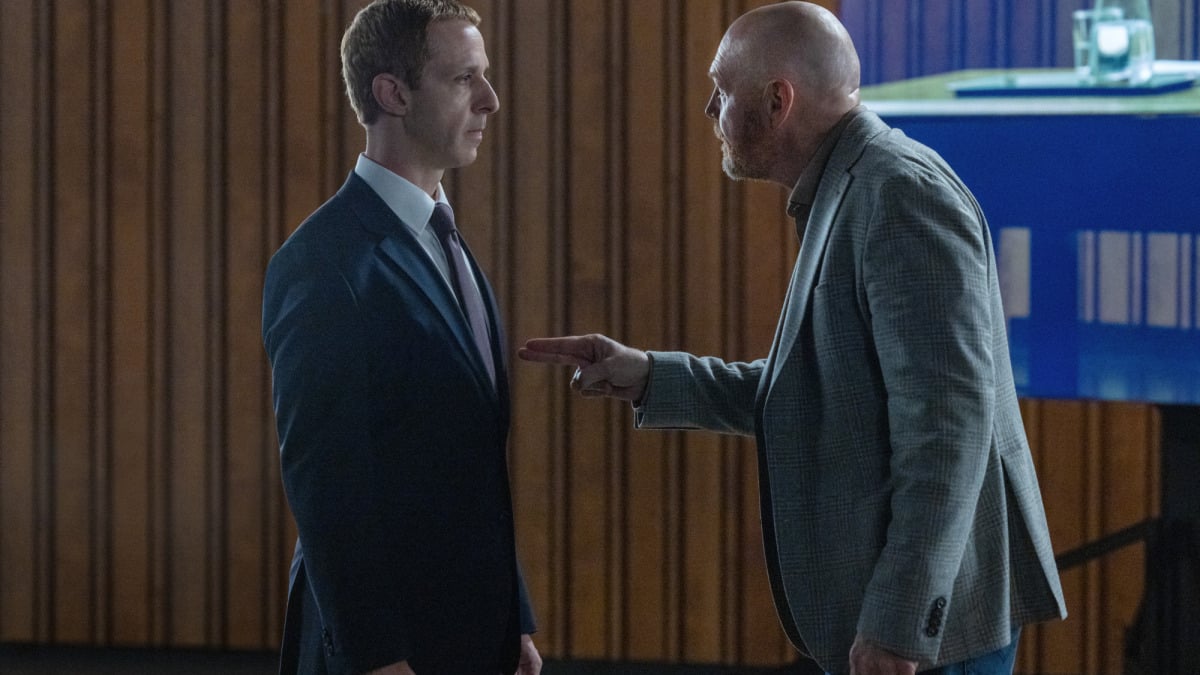
Through The Wall Street Journal‘s Jeff Horwitz (Jeremy Allen White) and Facebook whistleblower Frances Haugen (Mikey Madison), The Social Reckoning recounts the two years of work that made up the publication’s explosive 2021 series, The Facebook Files. The birth of the exposé, a series of insider accounts of Facebook’s decision to reroute its algorithm in service of polarizing extremism, is presented in two competing timelines.

In one, Huagen and Horwitz attempt to penetrate the Silicon Valley giant’s defenses to learn the true scope of its wrongdoing. In the other, CEO Mark Zuckerberg (Jeremy Strong) readies himself to testify before Congress — as Jan. 6th insurrectionists storm the Capitol.

So it’s strange that it’s characters — real-life journalists, brave whistleblowers, and profit-driven tech overlords who had a direct role in the current administration’s success — don’t say the name “Trump.”

Despite a third of the movie set in 2020, COVID-19 is largely referred to as “the novel virus.” The movie skirts the rampant medical misinformation, spread by conservative conspiracy groups, that flourished on Meta platforms.

The movie also omits the full details of Facebook’s startling algorithmic misconduct that surrounded and informed the events of The Social Reckoning. And that’s just the tip of the iceberg.

Meta IRL

In 2018, the tech giant was implicated in a massive data breach that harvested user profiles to target U.S. voters ahead of President Donald Trump’s 2016 election victory. Facebook had already been accused of a host of reported user privacy violations, including conducting an algorithm-based psychological study on unwitting users. Due to Facebook’s outsized role in spreading fake news, the company’s CEO was given the title “Misinformer of the Year” in 2017 by Media Matters for America. 

Civil rights organizations like GLAAD have long deemed Meta’s platforms unsafe for LGBTQ users. Facebook’s algorithm has not only helped foster discord on home soil, but is also alleged to have had a role in global cultural genocides by human rights groups like Amnesty International. 

Following Haugen’s real-life congressional testimony, used as the final beat of Sorkin’s film, the company was accused of exacerbating a youth mental health crisis, multiple deaths by suicide, and an explosion of real and synthetic child sexual abuse materials (CSAM). The first point is briefly touched on in the film, while the last is completely sidelined.

Three weeks after Haugen’s congressional appearance in 2021, Facebook changed its name to Meta. The company then underwent a brief public-image overhaul — until Trump came back into power. Following his reelection, Meta gave $1 million to Trump’s inauguration fund. 

The Social Reckoning implores someone, anyone, to act. The film posits that the federal government may be able to hold Zuckerberg to account.

It hasn’t. 

One character, a member of the company’s civic integrity team who helps leak internal reports about Instagram’s impact on teen mental health, tells Haugen that something needs to be done before the company proceeds with its plan for “Instagram Kids.” 

In 2024, Meta debuted Teen Accounts to address growing unease about young people’s online habits. Following studies that concluded the changes featured in Instagram’s Teen Accounts were ineffective, the company overhauled them. In the months since the overhaul, advocates have alleged Teen Accounts are still failing to curb online abuse. 

Another real-life whistleblower, Arturo Béjar, has continued to testify to Meta’s alleged intentional disregard for teen mental health in court. 

Will Meta change?

In the film’s epilogue, Sorkin describes Haugen’s disclosure as having “caused some pain” for the company.

“I would not call it a massive pain for Meta,” said Christine McComas, founding member of child safety advocacy group Parents for Safe Online Spaces (ParentsSOS). “It was a moment of clarity for people to understand what’s going on.”

Unlike Sorkin’s more timid portrayal, McComas describes Haugen as a person who knew what she needed to do. McComas credits Haugen with galvanizing the work of bereaved parents whose children had died by suicide following abusive social media interactions.


That is an inexcusable failure of leadership.

– Ashwin Verghese, Fairplay

As of publishing, more than 3,000 federal lawsuits have been filed against Meta alleging intentional harm to teen users. The film briefly mentions the work of attorneys general in amplifying these claims. Many of these cases are still ongoing or have settled out of court, but a few have resulted in surface level changes to Meta platforms.

Much like Teen Accounts, researchers argue the changes did not do enough to protect young users. 

Concerted pressure from state leaders and child safety advocates has finally pushed Meta to agree to more substantive reform, such as algorithmic guardrails. Still, most argue that comprehensive federal regulation is the only way to truly curb Meta’s harm. 

Congressional leaders have “completely failed” to hold Meta and its competitors accountable, says Ashwin Verghese, communications director of child safety nonprofit Fairplay. “In fact, Congress has not passed a bill focused on keeping kids safe online in nearly 30 years. That is an inexcusable failure of leadership,” Verghese said.

It has been years since the Wall Street Journal published The Facebook Files. To be fair to Sorkin, political change is slow. Courts have their limits when powerful, near monopolistic, companies are involved. 

But there’s a lingering question that the movie, given its timeline and broad topics, only mildly addresses through its luddite journalist, Horwitz: If Congress won’t act, why won’t we, as a society, just stop using Meta’s problematic products?

Meta, why can’t we quit you?

Compared to Horwitz, who is comedically introduced as someone who can’t even use a GPS, Sorkin depicts Haugen as an idealist, clinging to the democratizing potential of Facebook. Her movie self is a firm believer that the platform’s ability to foster social connection is a societal good. The character doesn’t rally for Meta’s shuttering, but for its reform. 

In early 2026, professor and marketing expert Scott Galloway called for an industry-wide boycott of tech platforms with disproportionate political and economic power. Included in that list were Meta platforms WhatsApp and Facebook (Instagram is also in Meta’s corporate roster). 

One year earlier, swaths of users threatened to delete their Meta accounts following platform changes that signaled its alignment with the Trump administration, including the erasure of hateful conduct protections for LGBTQ users and the shuttering of its fact checking program. Years before that, users attempted to galvanize change through the 2018 #DeleteFacebook trend.

Yet, even with these calls, Meta has yet to see a mass exodus of users. The company only recently reported a substantial decline in daily users across its platforms. The loss was just 20 million of a reported 3 billion users. After the launch of its new AI agent Muse, Meta regained almost 2 million daily users. 


Too many people are complacent because they don’t know an alternative.

– Sam Hiner, Young People’s Alliance

“Meta has spent millions of dollars in public relations campaigns to claim their platforms are safe while denying responsibility,” said Maurine Molak, advocate and co-founder of ParentsSOS. Molak was one of a group of survivor parents who received an apology from Zuckerberg during his 2024 congressional testimony. 

Molak argues that Meta’s billion-dollar PR spin has sowed confusion among parents, users, and even congressional leaders. Without clarity, users are more inclined to stay and avoid the pains of leaving.

“Too many people are complacent because they don’t know an alternative,” explained Sam Hiner, executive director of the youth-led advocacy nonprofit Young People’s Alliance. Hiner and Molak both argue one of the biggest hurdles to leaving Facebook is the Fear of Missing Out.

“If you’re not online, it feels like you’re missing out on an important cultural space,” said Hiner. “It’s also hard for competitors to emerge because of the network effect — all of my friends are on Meta platforms, not whatever competitor may emerge.”

Molak links this to Facebook’s role as one of the first social media platforms. Millions, perhaps billions of adults, have spent nearly two decades building their accounts on Facebook and more than a decade on Instagram. Recntly, they have merged these accounts onto Meta’s X-competitor Threads — a wave of users flocked to Threads after Elon Musk’s take over of Twitter. It was the lesser of two evils.

Meta platforms are part of many’s daily habit, maybe even their identity. With its foray into general AI and its diversification into massively popular chat platforms, users are getting wrenched deeper into Meta’s web. 

“Algorithms aren’t visible, so it’s understandably been quite difficult for most folks to connect the harms they experience in their communities — more people angry and outraged, more mental health problems, more anxious children — with some computer code designed in a faraway lab,” explained Julie Scelfo, founder and executive director of Mothers Against Media Addiction. 

This movie will not move the needle on Meta

Meta has not issued a statement on The Social Reckoning, and it probably never needs to. The film’s opening weekend was an unequivocal flop.

The company is shielded by its buying power. In an April earnings call, the tech giant said it brought in $56.3 billion, probably tied to its ongoing generative AI investments.

“The monetary fines imposed on Meta are comparable to parking tickets,” said Molak. In August, Meta settled out of a potentially consequential social media addiction lawsuit for the sum of $17 billion dollars — just one percent of its stock value, paid out over a decade. 

During one pivotal moment between Horwitz and Haugen in The Social Reckoning, Haugen ponders if it’s possible to push powerful people toward change. 

“When it’s about money, it’s hard,” says Horwitz. “When it’s not about money, it’s even harder.”

Recommended deals for you


HBO Max

—
top pick for premium content


Disney+

—
best for families


Hulu

—
popular choice for originals


Peacock

—
low-cost choice for live sport

Products available for purchase through affiliate links. If you buy something through links on our site, Mashable may earn an affiliate commission.
You Can Now Destroy Flock Cameras for Cash in GTA V


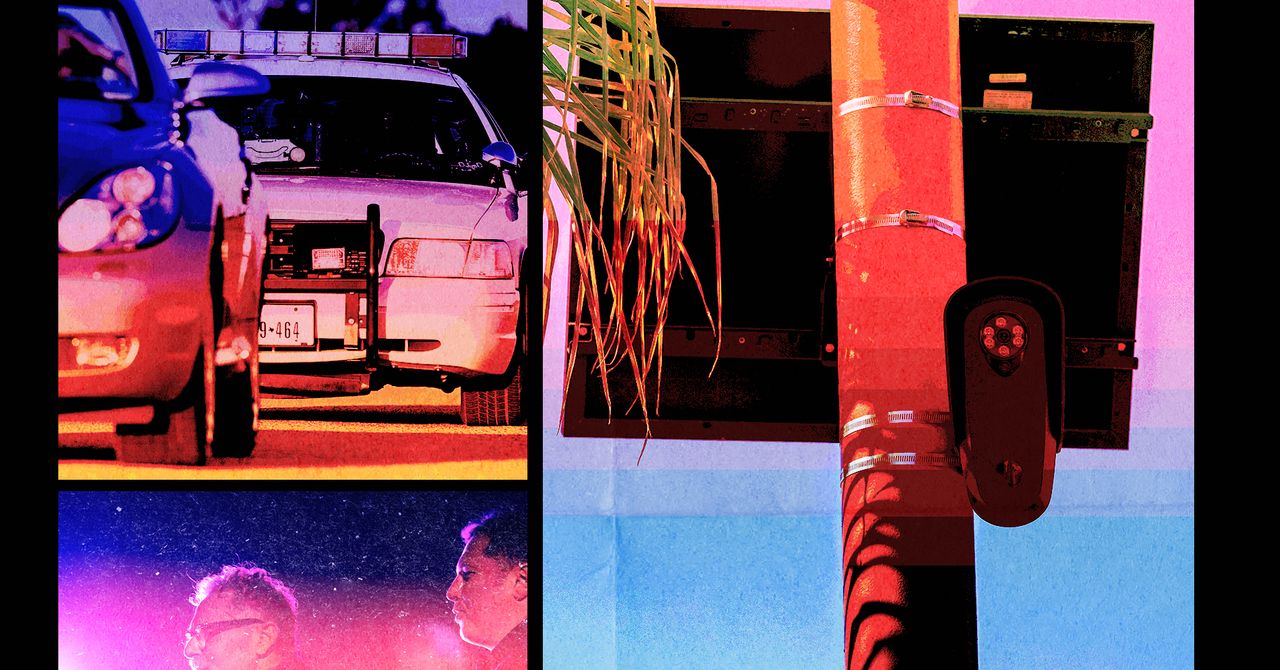
People are not happy about Flock Safety’s automated license plate readers and the cops that allegedly misuse them. If you’re one of those ALPR-haters, you can now take out your rage in the video game Grand Theft Auto V by installing Grand Theft Automated License Plate Reader, a mod built by artist Morry Kolman.

The mod installs 235 Flock cameras around the fictional Los Santos, a riff on the real-life city of Los Angeles. Players can smash and shoot down the cameras and get paid $600 for each one they destroy, which Kolman priced based on a teardown of a Flock Falcon Flex Camera by the Iowa-based civil liberties group Eyes Off of Cedar Rapids. The in-game cameras log every time a player destroys and drives by one, and players can render a photo album of their interactions.

In real life, vigilantes have allegedly wrecked Flock cameras in their communities using spray-paint, saws, bullets, and even flaming projectiles. An NPR analysis found that Flock cameras have been vandalized in at least 36 states.

“GTPLR is not an endorsement of the activities that it allows in the game in the same way that GTA is not an endorsement of the activities that are allowed in the game,” says Kolman, referring to the fact that GTA is largely about doing fictional crimes. “But I think there is a public appetite for some kind of cathartic release against these machines.”

In addition to being fun objects to destroy, the GTA cameras also operate as an extension of the police in-game. Passing by one of the 235 cameras while being chased by the cops prolongs the game’s cooldown period. Because of how dense the cameras are in some areas, it can make the game impossible to play.

There’s also a 5 percent chance that the cameras will trigger a random police response even if the player isn’t doing anything wrong, which Kolman says was inspired by news reports about innocent people being held at gunpoint because of ALPR errors.

“There are violent responses and really dangerous situations that are created by these cameras and their inaccuracies,” says Kolman.

Flock did not immediately respond to a request for comment for this story.

GTA V has been around for over a decade, and a rich modding community has built up around it (WIRED covered one back in 2015.) The long-awaited sequel, Grand Theft Auto VI, is slated to come out in November and will be set in a fictional version of Miami called Vice City.

Kolman doesn’t have specific plans to build a version of GTALPR for that, joking, “We’ll probably wait to see what the people of Vice City and their local government have already installed around their map.”

In real-life LA, the Los Angeles Police Department suspended its use of Flock cameras this summer following a recommendation from the LAPD’s inspector general. The tide is turning in other places too—governors in both Texas and Florida recently took steps to curtail the use of Flock cameras in their respective states, and across the US, there were 131 Flock contract terminations in August alone, according to the anti-surveillance advocacy group Secure Justice.

For all the fun that fake-smashing surveillance cameras can be, Kolman seriously hopes that players can feel the “insidiousness and inescapability of the surveillance” through GTALPR.

“I know that you could read a thousand articles about why surveillance is bad and why Flock is horrible,” says Kolman. “Or I could make you feel how pervasive these Flock cameras are by having you try to drive around the map of Los Santos.”

Fitness tracking under scrutiny as Strava military data leak exposes personnel


Your Strava runs might feel private, but a new Strava military data leak shows how easily that information can reveal more than your workout. In the latest case, activity logs have been linked to more than 500 UK military personnel, connecting everyday exercise to sensitive locations.

This goes beyond visible routes. Shared histories and account details can be combined to identify people and map where they live and work. Known locations become more revealing once behavior is layered on top.

A recent incident showed how a single tracked session revealed the position of a naval vessel. Routine posts can carry real consequences. The issue comes down to visibility and how much is left open by default.

Public runs tied to real people

The investigation uncovered shared routes connected to personnel across several UK bases, including Northwood, Faslane, and North Yorkshire. These weren’t abstract traces. Account histories made it possible to link sessions to specific individuals.

Once identified, an account can reveal habits, frequent routes, and social connections through shared features. That expands the scope quickly and makes tracking easier over time.

In one case, a run label hinted the user understood the risk, yet it stayed accessible. That gap between awareness and action is part of the problem. Analysts warn that small fragments of information can still be combined into something far more detailed.

Small details build a bigger picture

The real danger builds over time. Repeated uploads create a trackable footprint that becomes easier to follow with each new entry.

Even if locations aren’t secret, surrounding behavior adds meaning. Movement between sites, timing, and consistency can all be inferred. For an outside observer, that’s enough to map routines and spot patterns.

At a submarine base, shared logs helped identify personnel and even family members through linked accounts. That kind of exposure extends beyond the original user and makes the data more valuable.

One setting can reduce the risk

The fix is already available, but many users skip it. Strava includes privacy controls that limit who can view your sessions and routes. Leaving those settings unchanged keeps your activity visible by default.

Switching activities to private reduces exposure right away. It limits how easily routes can be traced and makes long-term patterns harder to build. Or you can check out other fitness apps.

The bigger takeaway applies to any fitness app that shares location data. If you use Strava, it’s worth checking your settings now and locking down what others can see. A small change can keep your routine from becoming a signal.

A Simple WhatsApp Security Flaw Exposed 3.5 Billion Phone Numbers


WhatsApp’s mass adoption stems in part from how easy it is to find a new contact on the messaging platform: Add someone’s phone number, and WhatsApp instantly shows whether they’re on the service, and often their profile picture and name, too.

Repeat that same trick a few billion times with every possible phone number, it turns out, and the same feature can also serve as a convenient way to obtain the cell number of virtually every WhatsApp user on earth—along with, in many cases, profile photos and text that identifies each of those users. The result is a sprawling exposure of personal information for a significant fraction of the world population.

One group of Austrian researchers have now shown that they were able to use that simple method of checking every possible number in WhatsApp’s contact discovery to extract 3.5 billion users’ phone numbers from the messaging service. For about 57 percent of those users, they also found that they could access their profile photos, and for another 29 percent, the text on their profiles. Despite a previous warning about WhatsApp’s exposure of this data from a different researcher in 2017, they say, the service’s parent company, Meta, still failed to limit the speed or number of contact discovery requests the researchers could make by interacting with WhatsApp’s browser-based app, allowing them to check roughly a hundred million numbers an hour.

The result would be “the largest data leak in history, had it not been collated as part of a responsibly conducted research study,” as the researchers describe it in a paper documenting their findings.

“To the best of our knowledge, this marks the most extensive exposure of phone numbers and related user data ever documented,” says Aljosha Judmayer, one of the researchers at the University of Vienna who worked on the study.

The researchers say they warned Meta about their findings in April and deleted their copy of the 3.5 billion phone numbers. By October, the company had fixed the enumeration problem by enacting a stricter “rate-limiting” measure that prevents the mass-scale contact discovery method the researchers used. But until then, the data exposure could have also been exploited by anyone else using the same scraping technique, adds Max Günther, another researcher from the university who cowrote the paper. “If this could be retrieved by us super easily, others could have also done the same,” he says.

In a statement to WIRED, Meta thanked the researchers, who reported their discovery through Meta’s “bug bounty” system, and described the exposed data as “basic publicly available information,” since profile photos and text weren’t exposed for users who opted to make it private. “We had already been working on industry-leading anti-scraping systems, and this study was instrumental in stress-testing and confirming the immediate efficacy of these new defenses,” writes Nitin Gupta, vice president of engineering at WhatsApp. Gupta adds, “We have found no evidence of malicious actors abusing this vector. As a reminder, user messages remained private and secure thanks to WhatsApp’s default end-to-end encryption, and no non-public data was accessible to the researchers.”

Security flaws in a carmaker’s web portal let one hacker remotely unlock cars from anywhere


A security researcher said flaws in a carmaker’s online dealership portal exposed the private information and vehicle data of its customers, and could have allowed hackers to remotely break into any of its customers’ vehicles.

Eaton Zveare, who works as a security researcher at software delivery company Harness, told TechCrunch the flaw he discovered allowed the creation of an admin account that granted “unfettered access” to the unnamed carmaker’s centralized web portal.

With this access, a malicious hacker could have viewed the personal and financial data of the carmaker’s customers, track vehicles, and enroll customers in features that allow owners — or the hackers — control some of their car’s functions from anywhere.

Zveare said he doesn’t plan on naming the vendor, but said it was a widely known automaker with several popular sub-brands. 

In an interview with TechCrunch ahead of his talk at the Def Con security conference in Las Vegas on Sunday, Zveare said the bugs put a spotlight on the security of these dealership systems, which grant their employees and associates broad access to customer and vehicle information.

Zveare, who has found bugs in carmakers’ customer systems and vehicle management systems before, found the flaw earlier this year as part of a weekend project, he told TechCrunch. 

He said while the security flaws in the portal’s login system was a challenge to find, once he found it, the bugs let him bypass the login mechanism altogether by permitting him to create a new “national admin” account. 

The flaws were problematic because the buggy code loaded in the user’s browser when opening the portal’s login page, allowing the user — in this case, Zveare — to modify the code to bypass the login security checks. Zveare told TechCrunch that the carmaker found no evidence of past exploitation, suggesting he was the first to find it and report it to the carmaker.

When logged in, the account granted access to more than 1,000 of the carmakers’ dealers across the United States, he told TechCrunch.

“No one even knows that you’re just silently looking at all of these dealers’ data, all their financials, all their private stuff, all their leads,” said Zveare, in describing the access.

Zveare said one of the things he found inside the dealership portal was a national consumer lookup tool that allowed logged-in portal users to look-up the vehicle and driver data of that carmaker. 

In one real-world example, Zveare took a vehicle’s unique identification number from the windshield of a car in a public parking lot and used the number to identify the car’s owner. Zveare said the tool could be used to look-up someone using only a customer’s first and last name.

With access to the portal, Zveare said it was also possible to pair any vehicle with a mobile account, which allows customers to remotely control some of their car’s functions from an app, such as unlocking their cars.

Zveare said he tried this out in a real-world example using a friend’s account and with their consent. In transferring ownership to an account controlled by Zveare, he said the portal requires only an attestation — effectively a pinky promise — that the user performing the account transfer is legitimate. 

“For my purposes, I just got a friend who consented to me taking over their car, and I ran with that,” Zveare told TechCrunch. “But [the portal] could basically do that to anyone just by knowing their name — which kind-of freaks me out a bit — or I could just look up a car in the parking lots.”

Zveare said he did not test whether he could drive away, but said the exploit could be abused by thieves to break into and steal items from vehicles, for example.

Another key problem with access to this carmaker’s portal was that it was possible to access other dealer’s systems linked to the same portal through single sign-on, a feature that allows users to login into multiple systems or applications with just one set of login credentials. Zveare said the carmaker’s systems for dealers are all interconnected so it’s easy to jump from one system to another.

With this, he said, the portal also had a feature that allowed admins, such as the user account he created, to “impersonate” other users, effectively allowing access to other dealer systems as if they were that user without needing their logins. Zveare said this was similar to a feature found in a Toyota dealer portal discovered in 2023.

“They’re just security nightmares waiting to happen,” said Zveare, speaking of the user-impersonation feature. 

Once in the portal Zveare found personally identifiable customer data, some financial information, and telematics systems that allowed the real-time location tracking of rental or courtesy cars, as well as cars being shipped across the country, and the option to cancel them — though, Zveare didn’t try.

Zveare said the bugs took about a week to fix in February 2025 soon after his disclosure to the carmaker.

“The takeaway is that only two simple API vulnerabilities blasted the doors open, and it’s always related to authentication,” said Zveare. “If you’re going to get those wrong, then everything just falls down.”

Cybersecurity Professor Faced China-Funding Inquiry Before Disappearing, Sources Say


Jason Covert, one of attorneys representing Xiaofeng Wang and his wife, Nianli Ma, a library systems analyst whose employee profile was also removed by Indiana University, tells WIRED that Wang and Ma are both “safe” and that neither of them have been arrested. Their legal team is not currently aware of any pending criminal charges against them, and while the couple’s attorneys have viewed a search warrant from the Department of Justice, Covert says they have not received a copy of the affidavit establishing probable cause.

Wang is considered among the top researchers in the field of privacy, data security, and biometric privacy, and his sudden disappearance came as a shock to many of his academic peers. Wang joined IU in 2004 and is the lead principal investigator of the multidisciplinary Center for Distributed Confidential Computing, which he established in 2022 with an almost $3 million grant from the National Science Foundation (NSF), according to a since-deleted bio on IU’s website. As part of his application for the NSF funding and other US federal research grants, Wang would have been required to disclose other grants he already received or were currently pending review.

On March 28, the FBI searched two home addresses associated with Wang. The same day, IU also reportedly terminated Wang’s job via an email sent by provost Rahul Shrivastav, which WIRED obtained and was first reported by The Indiana Daily Student. The email also said it was understood that Wang had recently accepted a position with a university in Singapore, a detail also repeated in the statement attributed to Li.

The statement says Wang planned to start at the unnamed Singaporean university on June 1, 2025 and requested a leave of absence from Indiana University in early March. But IU responded by “putting him on administrative leave, removing his IU homepage, and disabling his IU email address,” it claims.

Wang’s new job offer “would be irrelevant in any event because it is for [the] next academic year and would not justify firing him,” Tanford says. Terminating his employment via an email was a violation of university policy, Tanford claims, which prohibits firing a tenured professor without cause, and requires a 10-day notice and a hearing before a faculty board of review, if requested by the staff member. “The faculty is deeply concerned. If the administration can fire a tenured professor without due process and in violation of a policy approved by our trustees, none of us is safe,” he says.

Reached for comment, an IU spokesperson declined to answer detailed questions from WIRED about prior communications between the university and Wang and the school’s decision to fire him.

“Indiana University was recently made aware of a federal investigation of an Indiana University faculty member,” university spokesperson Mark Bode tells WIRED in an emailed statement. “At the direction of the FBI, Indiana University will not make any public comments regarding this investigation. In accordance with Indiana University practices, Indiana University will also not make any public comments regarding the status of this individual.”

Trump’s Spy Chief Urged to Declassify Details of Secret Surveillance Program


Senator Ron Wyden of Oregon, a renowned privacy hawk who has served on the Senate intelligence committee since just after 9/11, has referred to the new provision as “one of the most dramatic and terrifying expansions of government surveillance authority in history.”

Declassifying the new types of businesses that can actually be considered an ECSP is an essential step in bringing about clarity to an otherwise nebulous change in federal surveillance practices, according to the ACLU and the other organizations joined in its effort. “Without such basic transparency, the law will likely continue to permit sweeping NSA surveillance on domestic soil that threatens the civil liberties of all Americans,” the groups wrote in their letter to Gabbard this week.

The Office of the Director of National Intelligence did not respond to multiple requests for comment.

In addition to urging Gabbard to declassify details about the reach of the 702 program, the ACLU and others are currently pressing Gabbard to publish information to quantify just how many Americans have been “incidentally” wiretapped by their own government. Intelligence officials have long claimed that doing so would be “impossible,” as any analysis of the wiretaps would involve the government accessing them unjustifiably, effectively violating those Americans’ rights.

The privacy groups, however, point to research published in 2022 out of Princeton University, which details a methodology that could effectively solve that issue. “The intelligence community’s refusal to produce the requested estimate undermines trust and weakens the legitimacy of Section 702,” the groups say.

Gabbard is widely reported to have softened her stance against government spying while working to secure her new position as director of the nation’s intelligence apparatus. During the 116th Congress, for instance, Gabbard introduced legislation that sought to completely dismantle the Section 702 program, which is considered the “crown jewel” or US intelligence collection and crucial to keeping tabs on foreign threats abroad, including terrorist organizations and cybersecurity threats—exhibiting a stance far more extreme than those traditionally held by lawmakers and civil society organizations who’ve long campaigned for surveillance reform.

While begging off from this position in January, Gabbard’s newly espoused views have, in fact, brought her more closely in line with mainstream reformers. In response to questions from the US Senate ahead of her confirmation, for example, Gabbard backed the idea of requiring the Federal Bureau of Investigation to obtain warrants before accessing the communications of Americans swept up by the 702 program.

Slews of national security hawks from former House speaker Nancy Pelosi to former House intelligence committee chairman Mike Turner have long opposed this warrant requirement, as traditionally have all directors of the FBI. “This warrant requirement strengthens the [intelligence community] by ensuring queries are targeted and justified,” Gabbard wrote in response to Senate questions in late January.

The Section 702 program was reauthorized last spring, but only for an additional two years. Early discussions about reauthorizing the program once more are expected to kick off again as early as this summer.

Sean Vitka, executive director of Demand Progress, one of the organizations involved in the lobbying effort, notes that Gabbard has a long history of supporting civil liberties, and refers to her recent statements about secret surveillance programs “encouraging.” “Congress needs to know, and the public deserves to know, what Section 702 is being used for,” Vitka says, “and how many Americans are swept up in that surveillance.”

“Section 702 has been repeatedly used to conduct warrantless surveillance on Americans, including journalists, activists, and even members of Congress,” adds Kia Hamadanchy, senior policy counsel for the ACLU. “Declassifying critical information, as well as providing long-overdue basic data about the number of US persons whose communications are collected under this surveillance are essential steps to increasing transparency as the next reauthorization debate approaches.”

Report finds most subscription services manipulate customers with ‘dark patterns’


Most subscription sites use “dark patterns” to influence customer behavior around subscriptions and personal data, according to a pair of new reports from global consumer protection groups. Dark patterns are “practices commonly found in online user interfaces [that] steer, deceive, coerce or manipulate consumers into making choices that often are not in their best interests.” The international research efforts were conducted by the International Consumer Protection and Enforcement Network (ICPEN) and the Global Privacy Enforcement Network (GPEN).

The ICPEN conducted the of 642 websites and mobile apps with a subscription component. The assessment revealed one dark pattern in use at almost 76 percent of the platforms, and multiple dark patterns at play in almost 68 percent of them. One of the most common dark patterns discovered was sneaking, where a company makes potentially negative information difficult to find. ICPEN said 81 percent of the platforms with automatic subscription renewal kept the ability for a buyer to turn off auto-renewal out of the purchase flow. Other dark patterns for subscription services included interface interference, where desirable actions are easier to perform, and forced action, where customers have to provide information to access a particular function.

The companion from GPEN examined dark patterns that could encourage users to compromise their privacy. In this review, nearly all of the more than 1,000 websites and apps surveyed used a deceptive design practice. More than 89 percent of them used complex and confusing language in their privacy policies. Interface interference was another key offender here, with 57 percent of the platforms making the least protective privacy option the easiest to choose and 42 percent using emotionally charged language that could influence users.

Even the most savvy of us can be influenced by these subtle cues to make suboptimal decisions. Those decisions might be innocuous ones, like forgetting that you’ve set a service to auto-renew, or they might put you at risk by encouraging you to reveal more personal information than needed. The reports didn’t specify whether the dark patterns were used in illicit or illegal ways, only that they were present. The dual release is a stark reminder that digital literacy is an essential skill.